How to Disable Brute-Force Rules in Vulnerability Scanning
Last updated: November 16, 2026
An exclusion stops Astra's automated scanner from reporting one scanner rule on a target in later scans. The main reason to use exclusions is brute-force rules: checks that deliberately send many login, password-reset or enumeration requests, and that can cause problems in the environment being scanned.
Why brute-force rules are the main use case
Brute-force rules test whether the application limits repeated attempts, for example many logins with wrong passwords or many password-reset requests.
Teams usually give Astra an environment where rate limiting and similar restrictions are removed, so the scanner can reach and test every page.
In that environment, brute-force rules are expected to be triggered, because the protection they look for was removed on purpose. The repeated attempts can also disrupt the environment, for example by locking test accounts.
Whenever one of these rules is triggered, exclude it from the finding. The rule is then excluded from all future scans on that target.
The brute-force and enumeration rules are:
Email Enumeration in Login Page
Bruteforceable Login Page
Missing Rate Limit on Forgot Password
Possible Name Enumeration
Excluding these rules affects only these checks. All other checks, such as XSS, SQL injection and misconfigurations, keep running as usual.
Note
If the organization's compliance requirements call for brute-force testing, review them before excluding these rules. Other ways to keep scans from tripping rate limits are covered in How to prevent scans from triggering rate limits and account lockouts.
Exclude a rule from a finding
Exclusions are added from a vulnerability that an automated scan has reported, by marking it as a false positive or accepting the risk. Users who can update vulnerability statuses, such as a Workspace Full Member, can add and change exclusions. Read-only roles can view them but not change them.
Open the vulnerability, for example Bruteforceable Login Page, from the Vulnerabilities page or the scan's Vulnerabilities tab.
Click Mark False Positive or Accept Risk.
Enter a reason, for example that rate limiting is turned off in the scanned environment. It's required for a false positive.
Keep Exclude from future scans switched on and choose All endpoints.
Click Mark False Positive or Accept Risk to confirm.
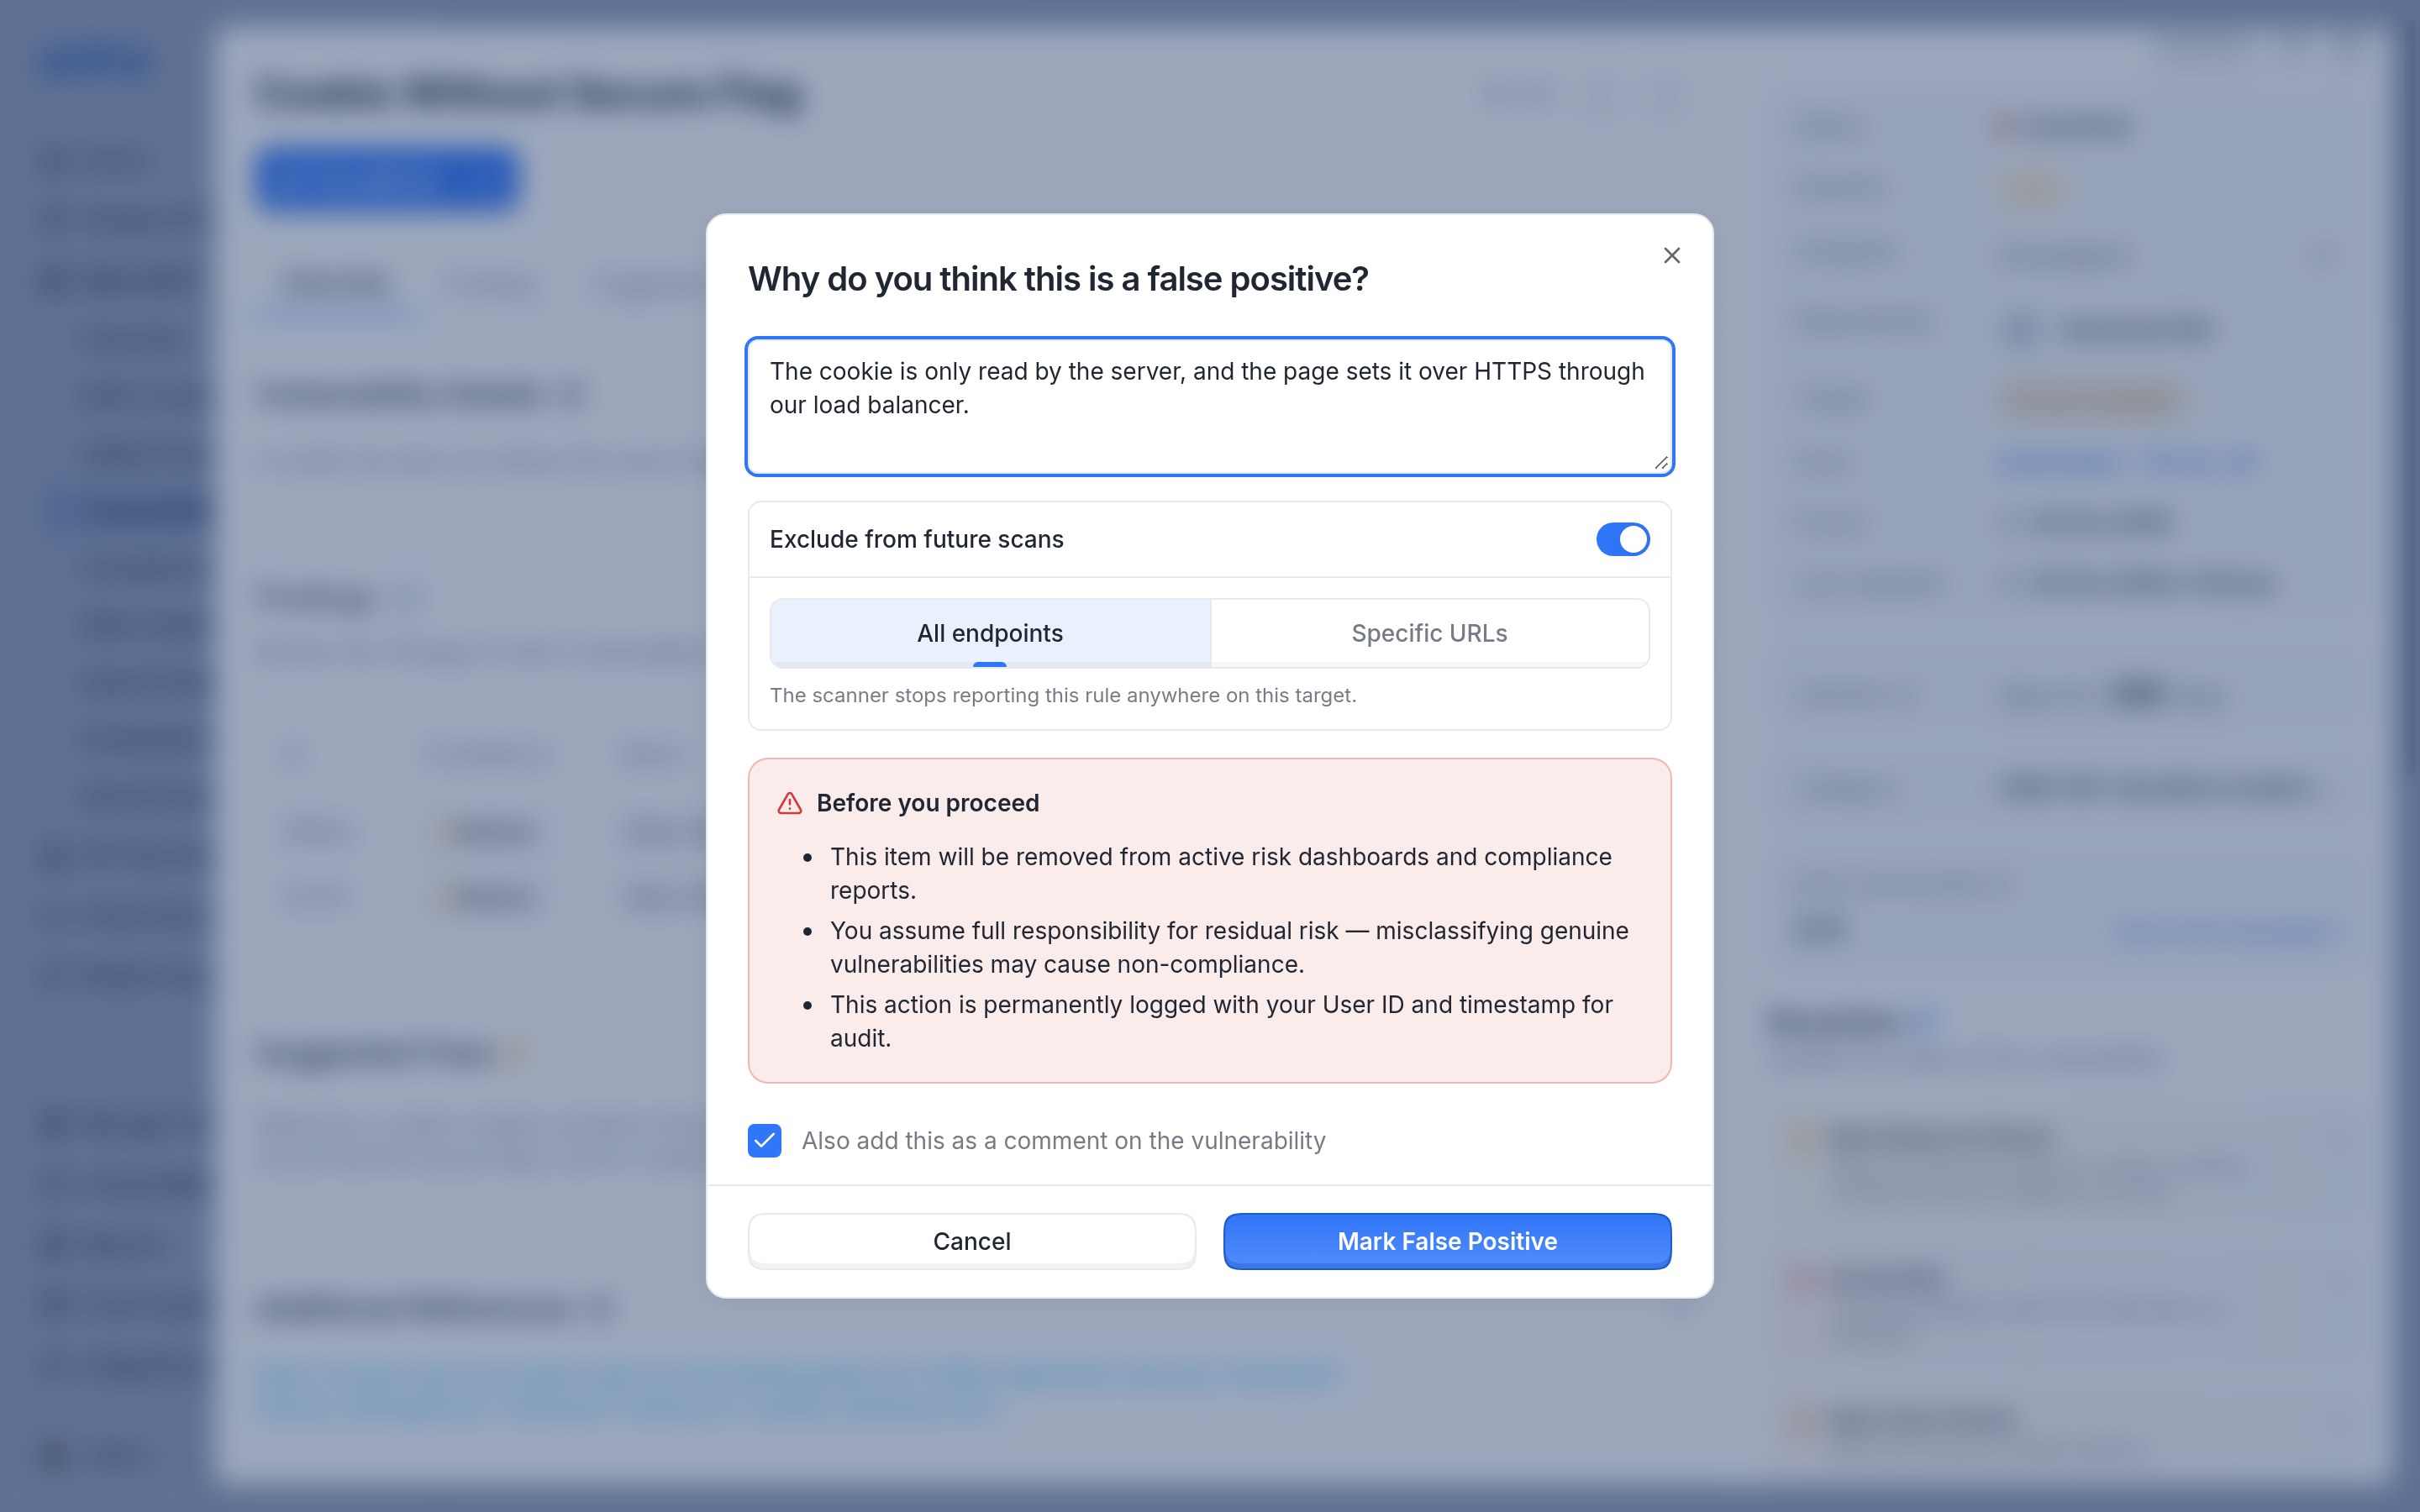
The false positive dialog, with Exclude from future scans switched on and All endpoints selected.
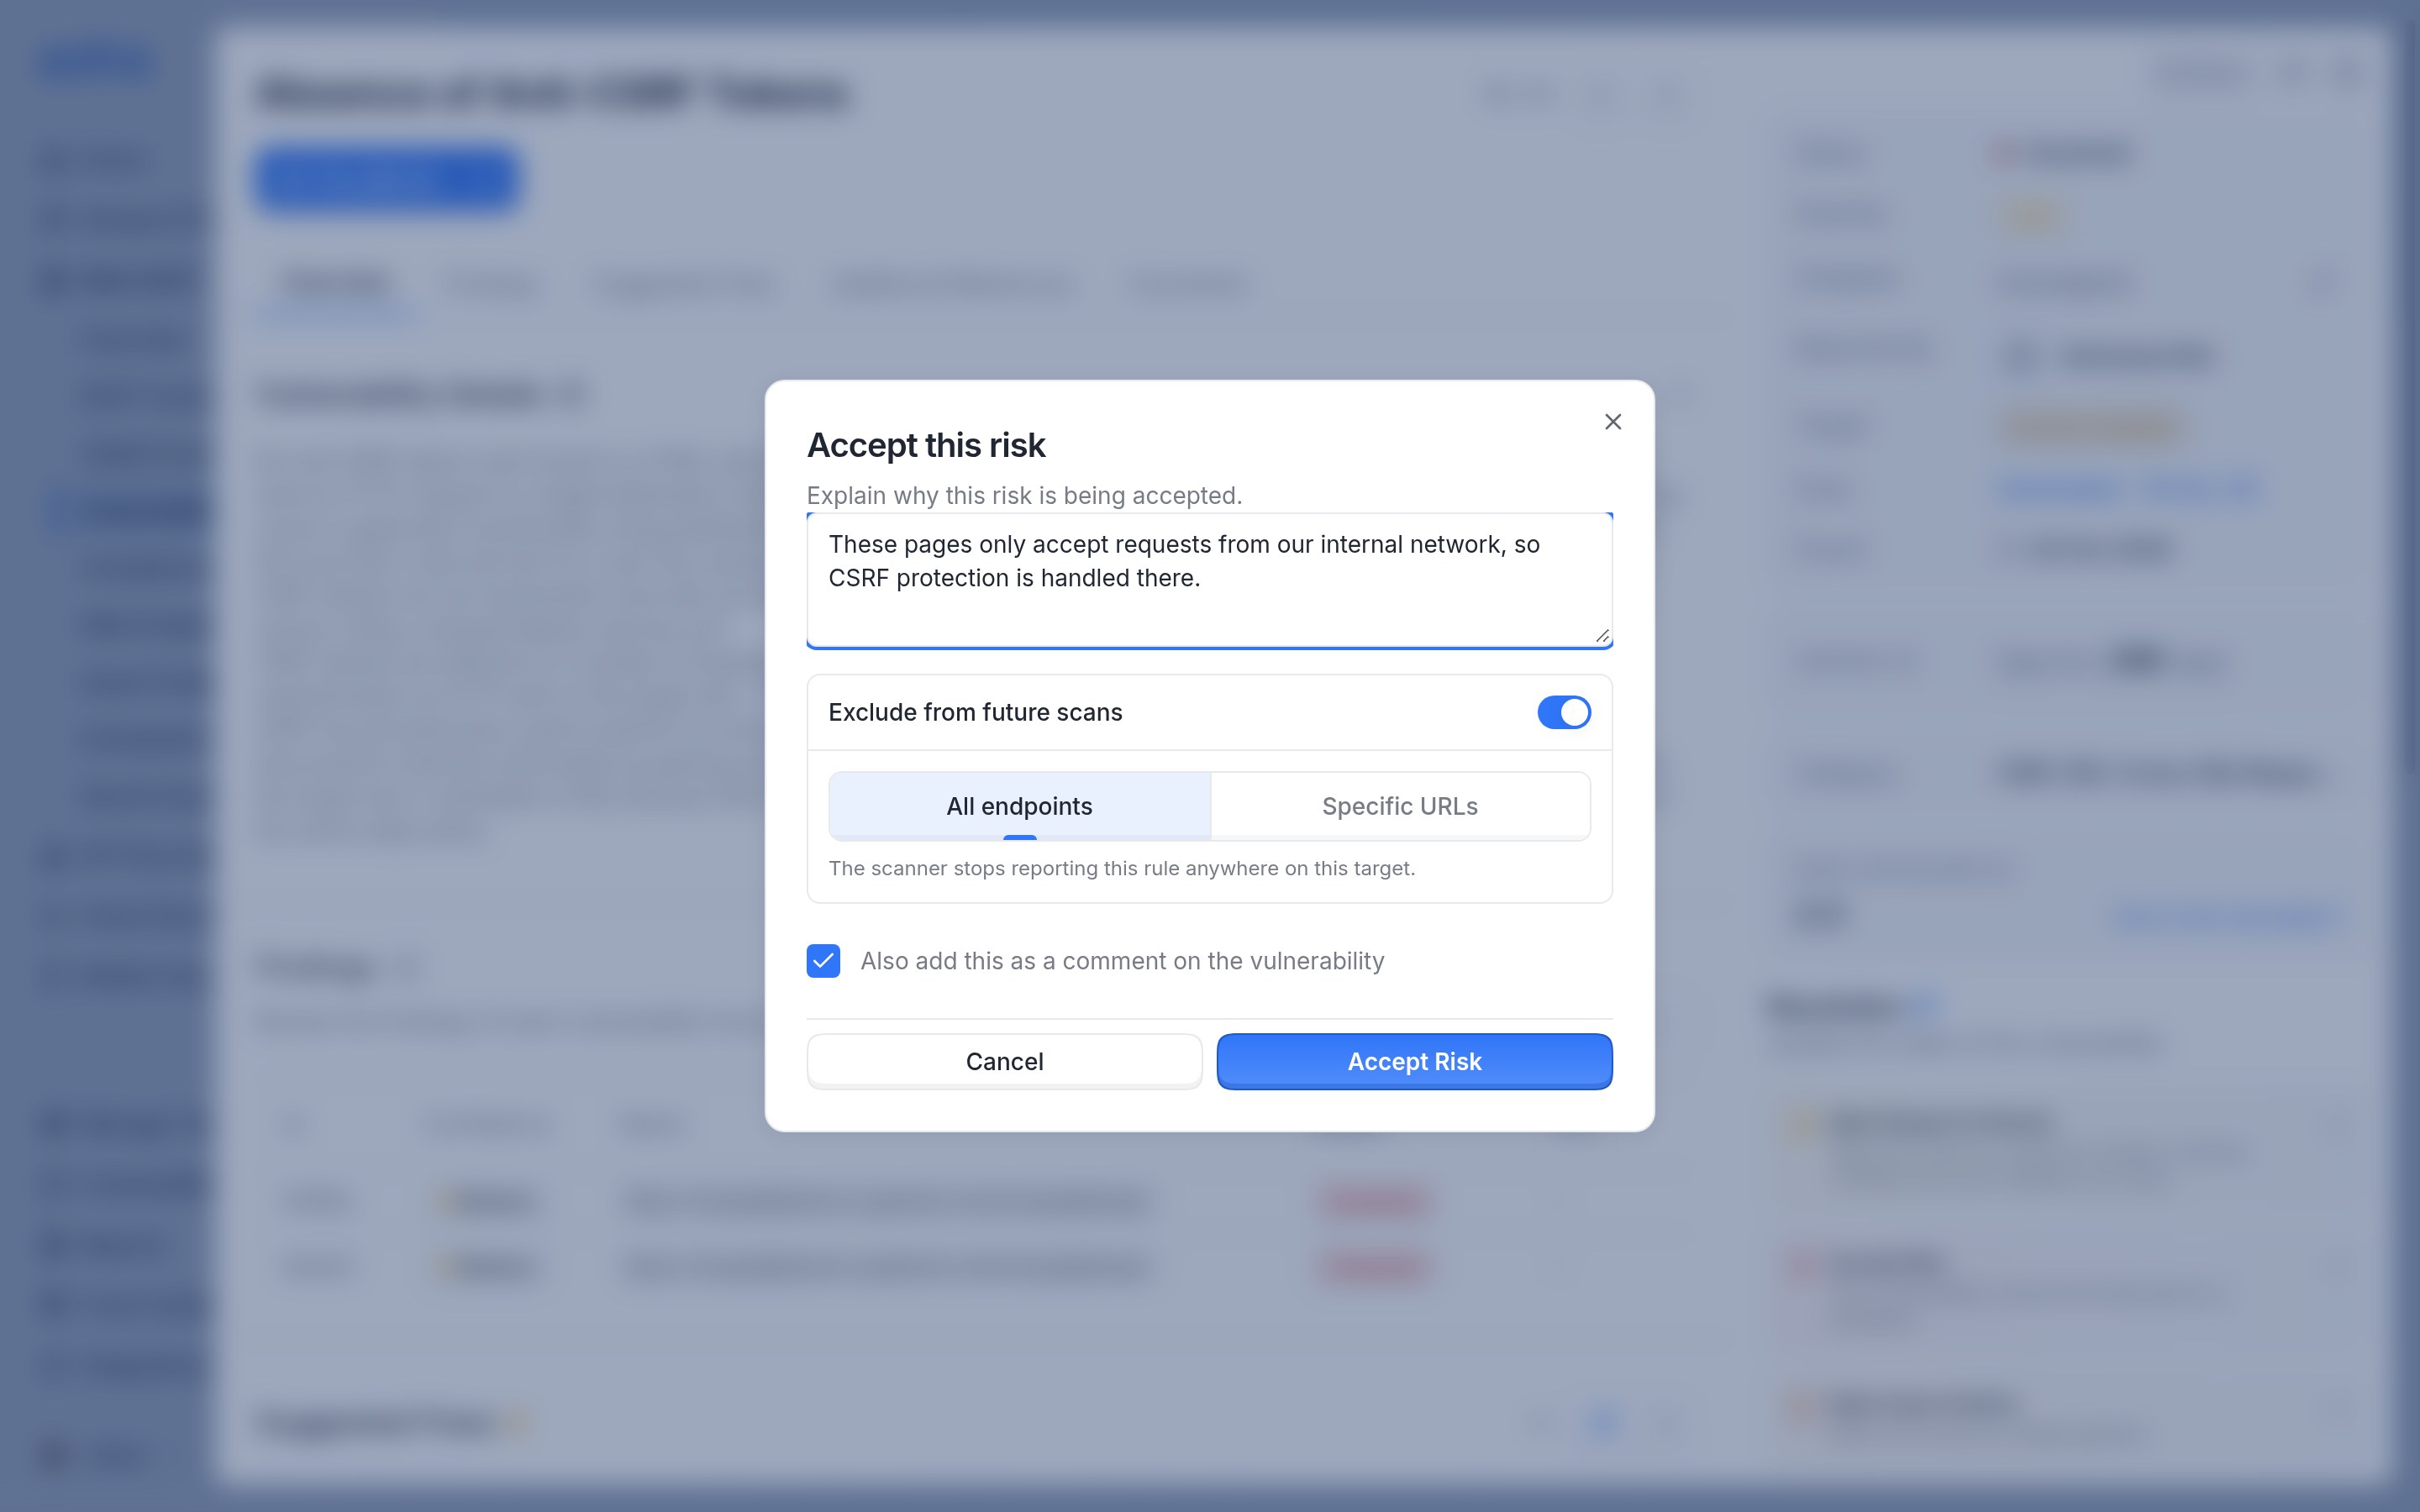
The Accept this risk dialog, with Exclude from future scans set to All endpoints.
The rule is added to the target's Excluded Scan Rules. The exclusion applies as soon as it's saved, including to a scan that's already running. With All endpoints, new scans on that target don't run the rule at all. Findings already reported stay as they are, and other targets keep testing for the rule.
Note
An exclusion can only be added from a finding. To exclude a brute-force rule before it has been triggered on a target, contact Astra's support team with the target name and the rules to exclude.
Choose where the rule is excluded
Exclude from future scans has two options:
All endpoints: the scanner stops reporting the rule anywhere on the target. This is the usual choice for brute-force rules.
Specific URLs: the scanner stops reporting the rule only at the URLs in the list, such as the login and forgot-password pages. The rule stays on for every other URL.
The switch is on by default when the target has no exclusion for the rule yet. Switch it off to change the status without affecting future scans.
To exclude the rule at specific URLs:
Click Specific URLs.
Pick a match type, enter the URL and click Add, or press Enter. Repeat for each URL.
To add many URLs at once, paste them into the field, one per line or separated by commas. Duplicates are skipped.
Change a URL or its match type in its row, or remove it with the × next to it. Then confirm the dialog.
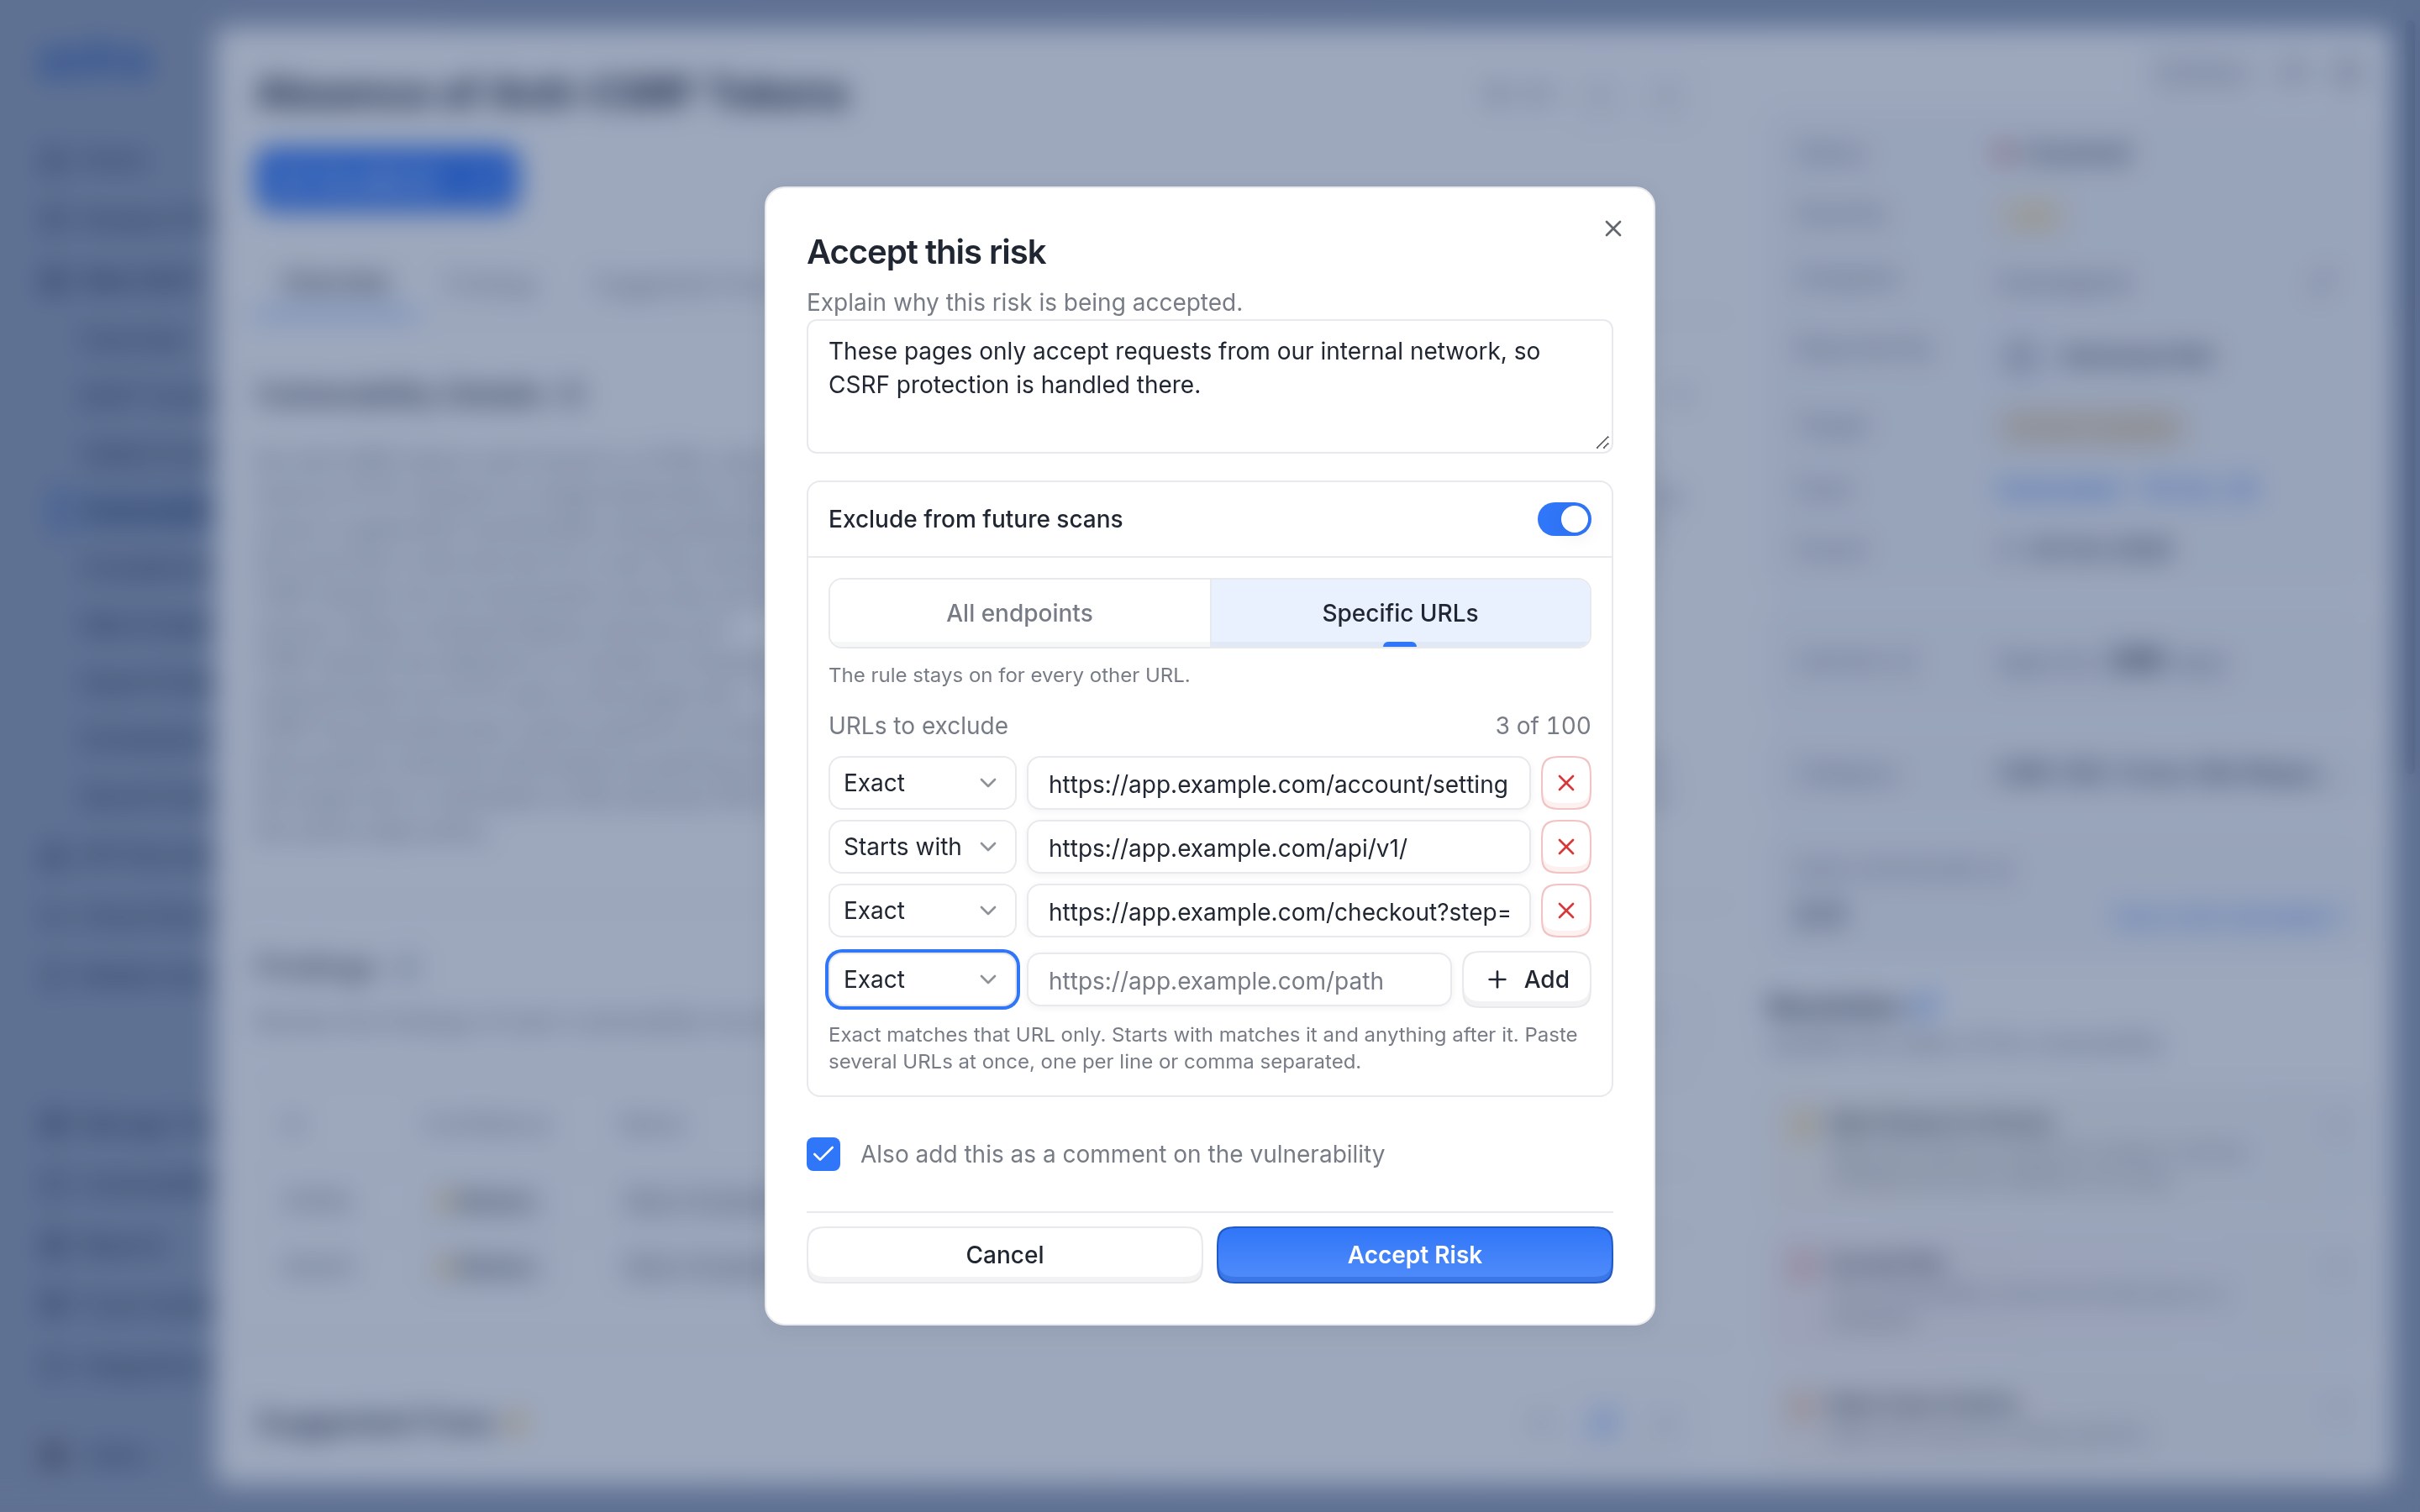
Specific URLs with three URLs in the list, one of them set to Starts with.
Each URL has its own match type:
Exact matches that URL only, including its query string. For example,
https://app.example.com/checkout?step=2doesn't coverhttps://app.example.com/checkout?step=3.Starts with matches the URL and anything after it at the next
/,?,#or&. For example,https://app.example.com/apicovershttps://app.example.com/api/usersandhttps://app.example.com/api?page=2, but nothttps://app.example.com/apiary.
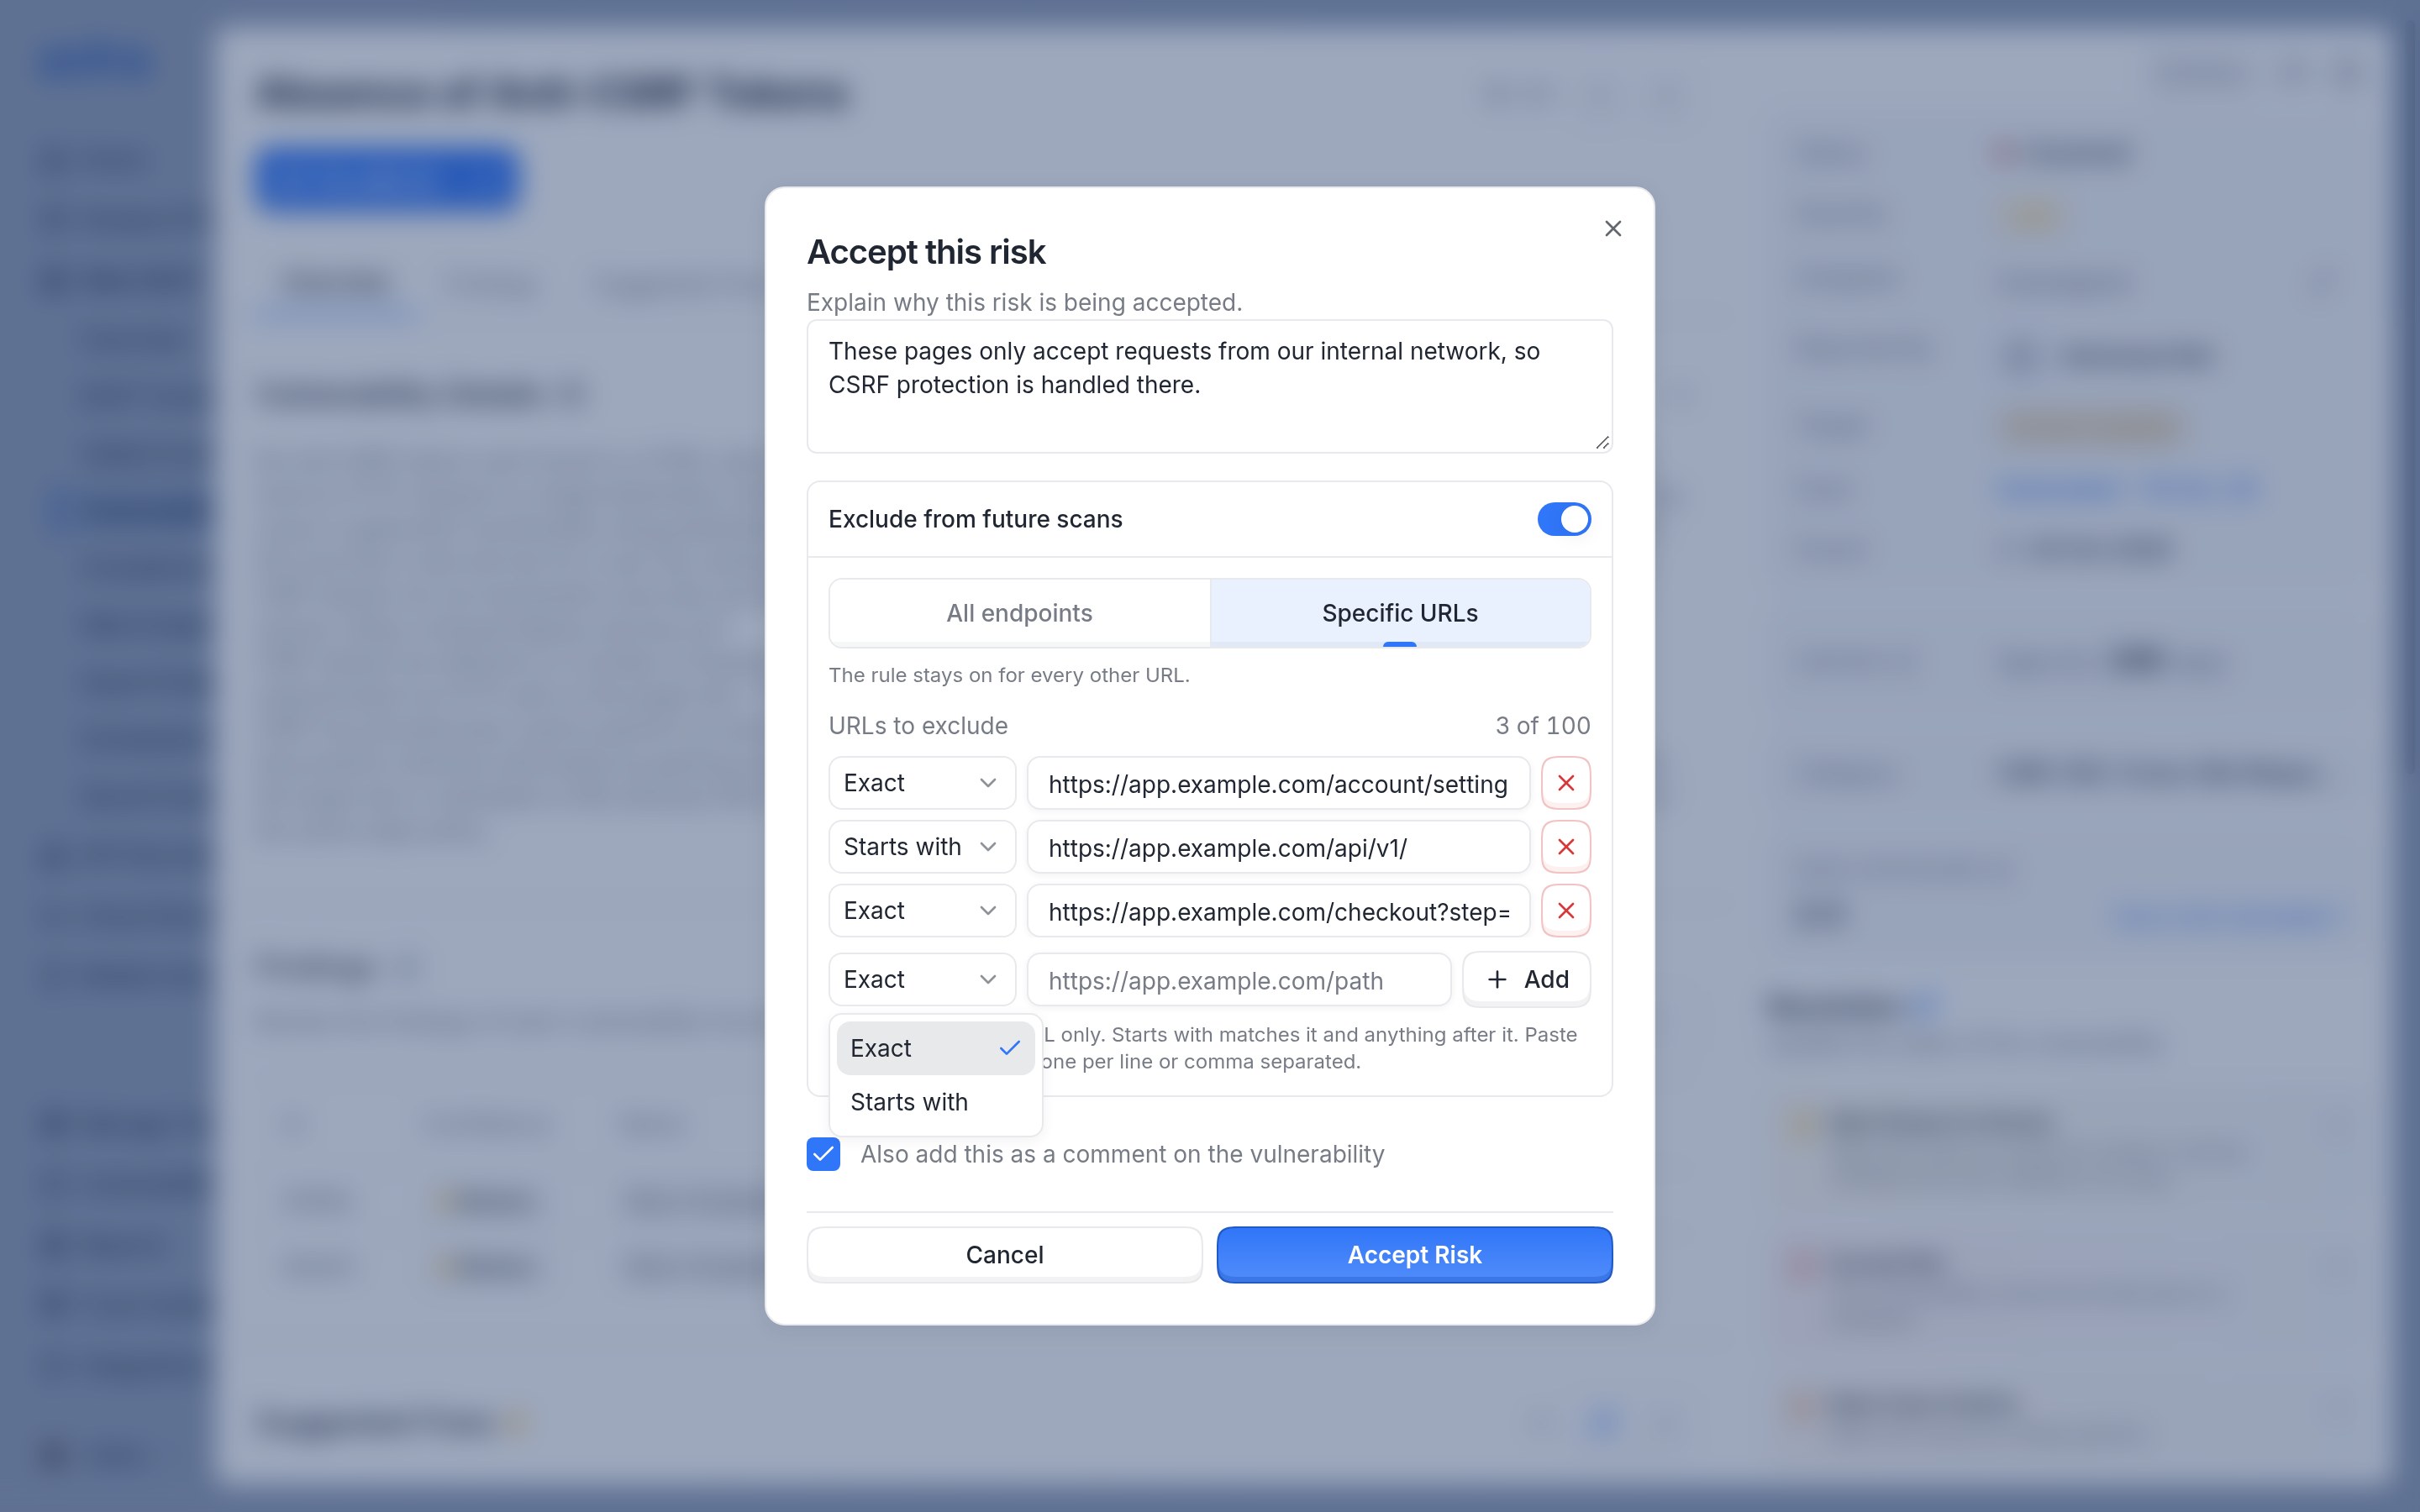
Each URL can be set to Exact or Starts with.
The list has a few rules. If a URL breaks one, the message shows under its row and the dialog can't be saved until it's fixed.
A rule holds at least 1 and at most 100 URLs. The counter above the list shows how many are used, for example 3 of 100.
Each URL must be a full http or https address, like
https://app.example.com/login, and can be up to 1,000 characters.A URL can be in the list only once.
Starts with can't be used on the site root alone, such as
https://app.example.com, because it would skip the whole site. Use All endpoints instead.
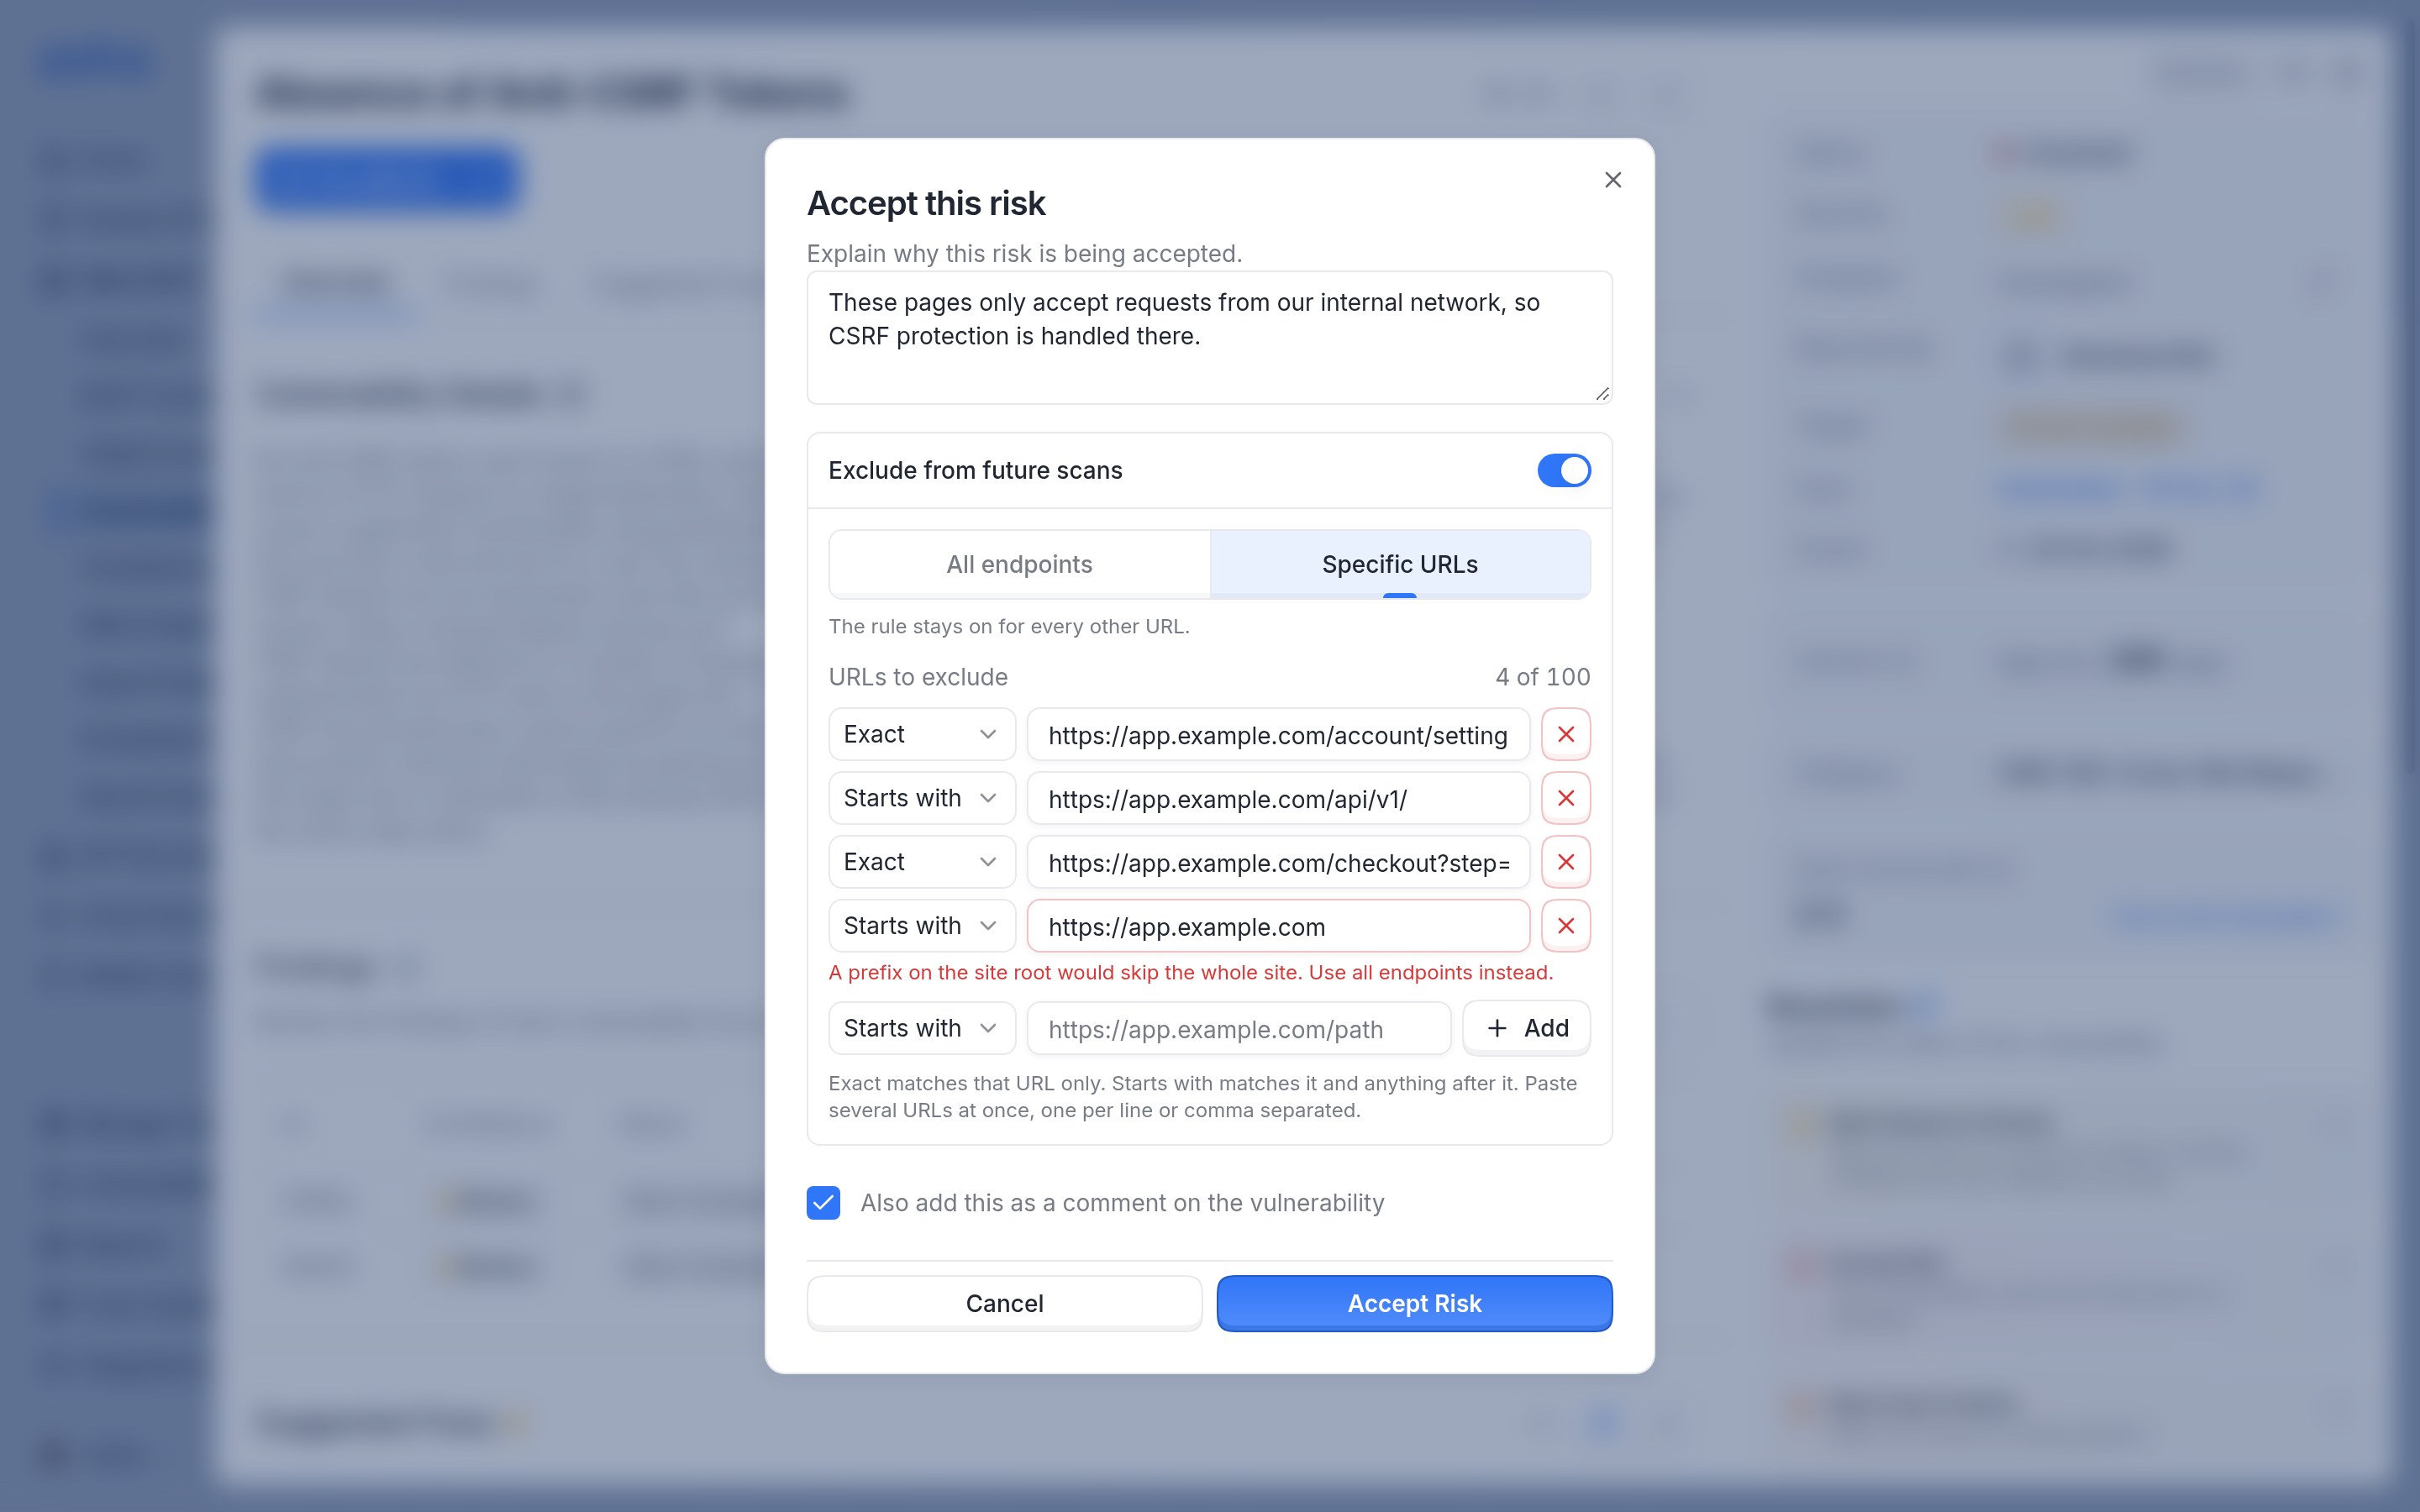
A Starts with URL on the site root shows an error under its row.
When the target already has an exclusion for this rule. The switch isn't shown, and saving the dialog updates the existing exclusion instead of creating a second one. The dialog shows the URLs already saved and a note on what saving will do:
New URLs are added to the saved list. Removing or changing a saved URL replaces the list.
Choosing All endpoints for a rule that skips specific URLs replaces those URLs, so the rule is skipped everywhere.
Choosing Specific URLs for a rule that's off on all endpoints turns scanning back on everywhere else. The dialog asks Limit this rule to specific URLs? first. Click Limit to these URLs to go ahead.
If the exclusion is paused, the note says This rule is paused, so scans are not skipping it. Saving doesn't turn it back on.
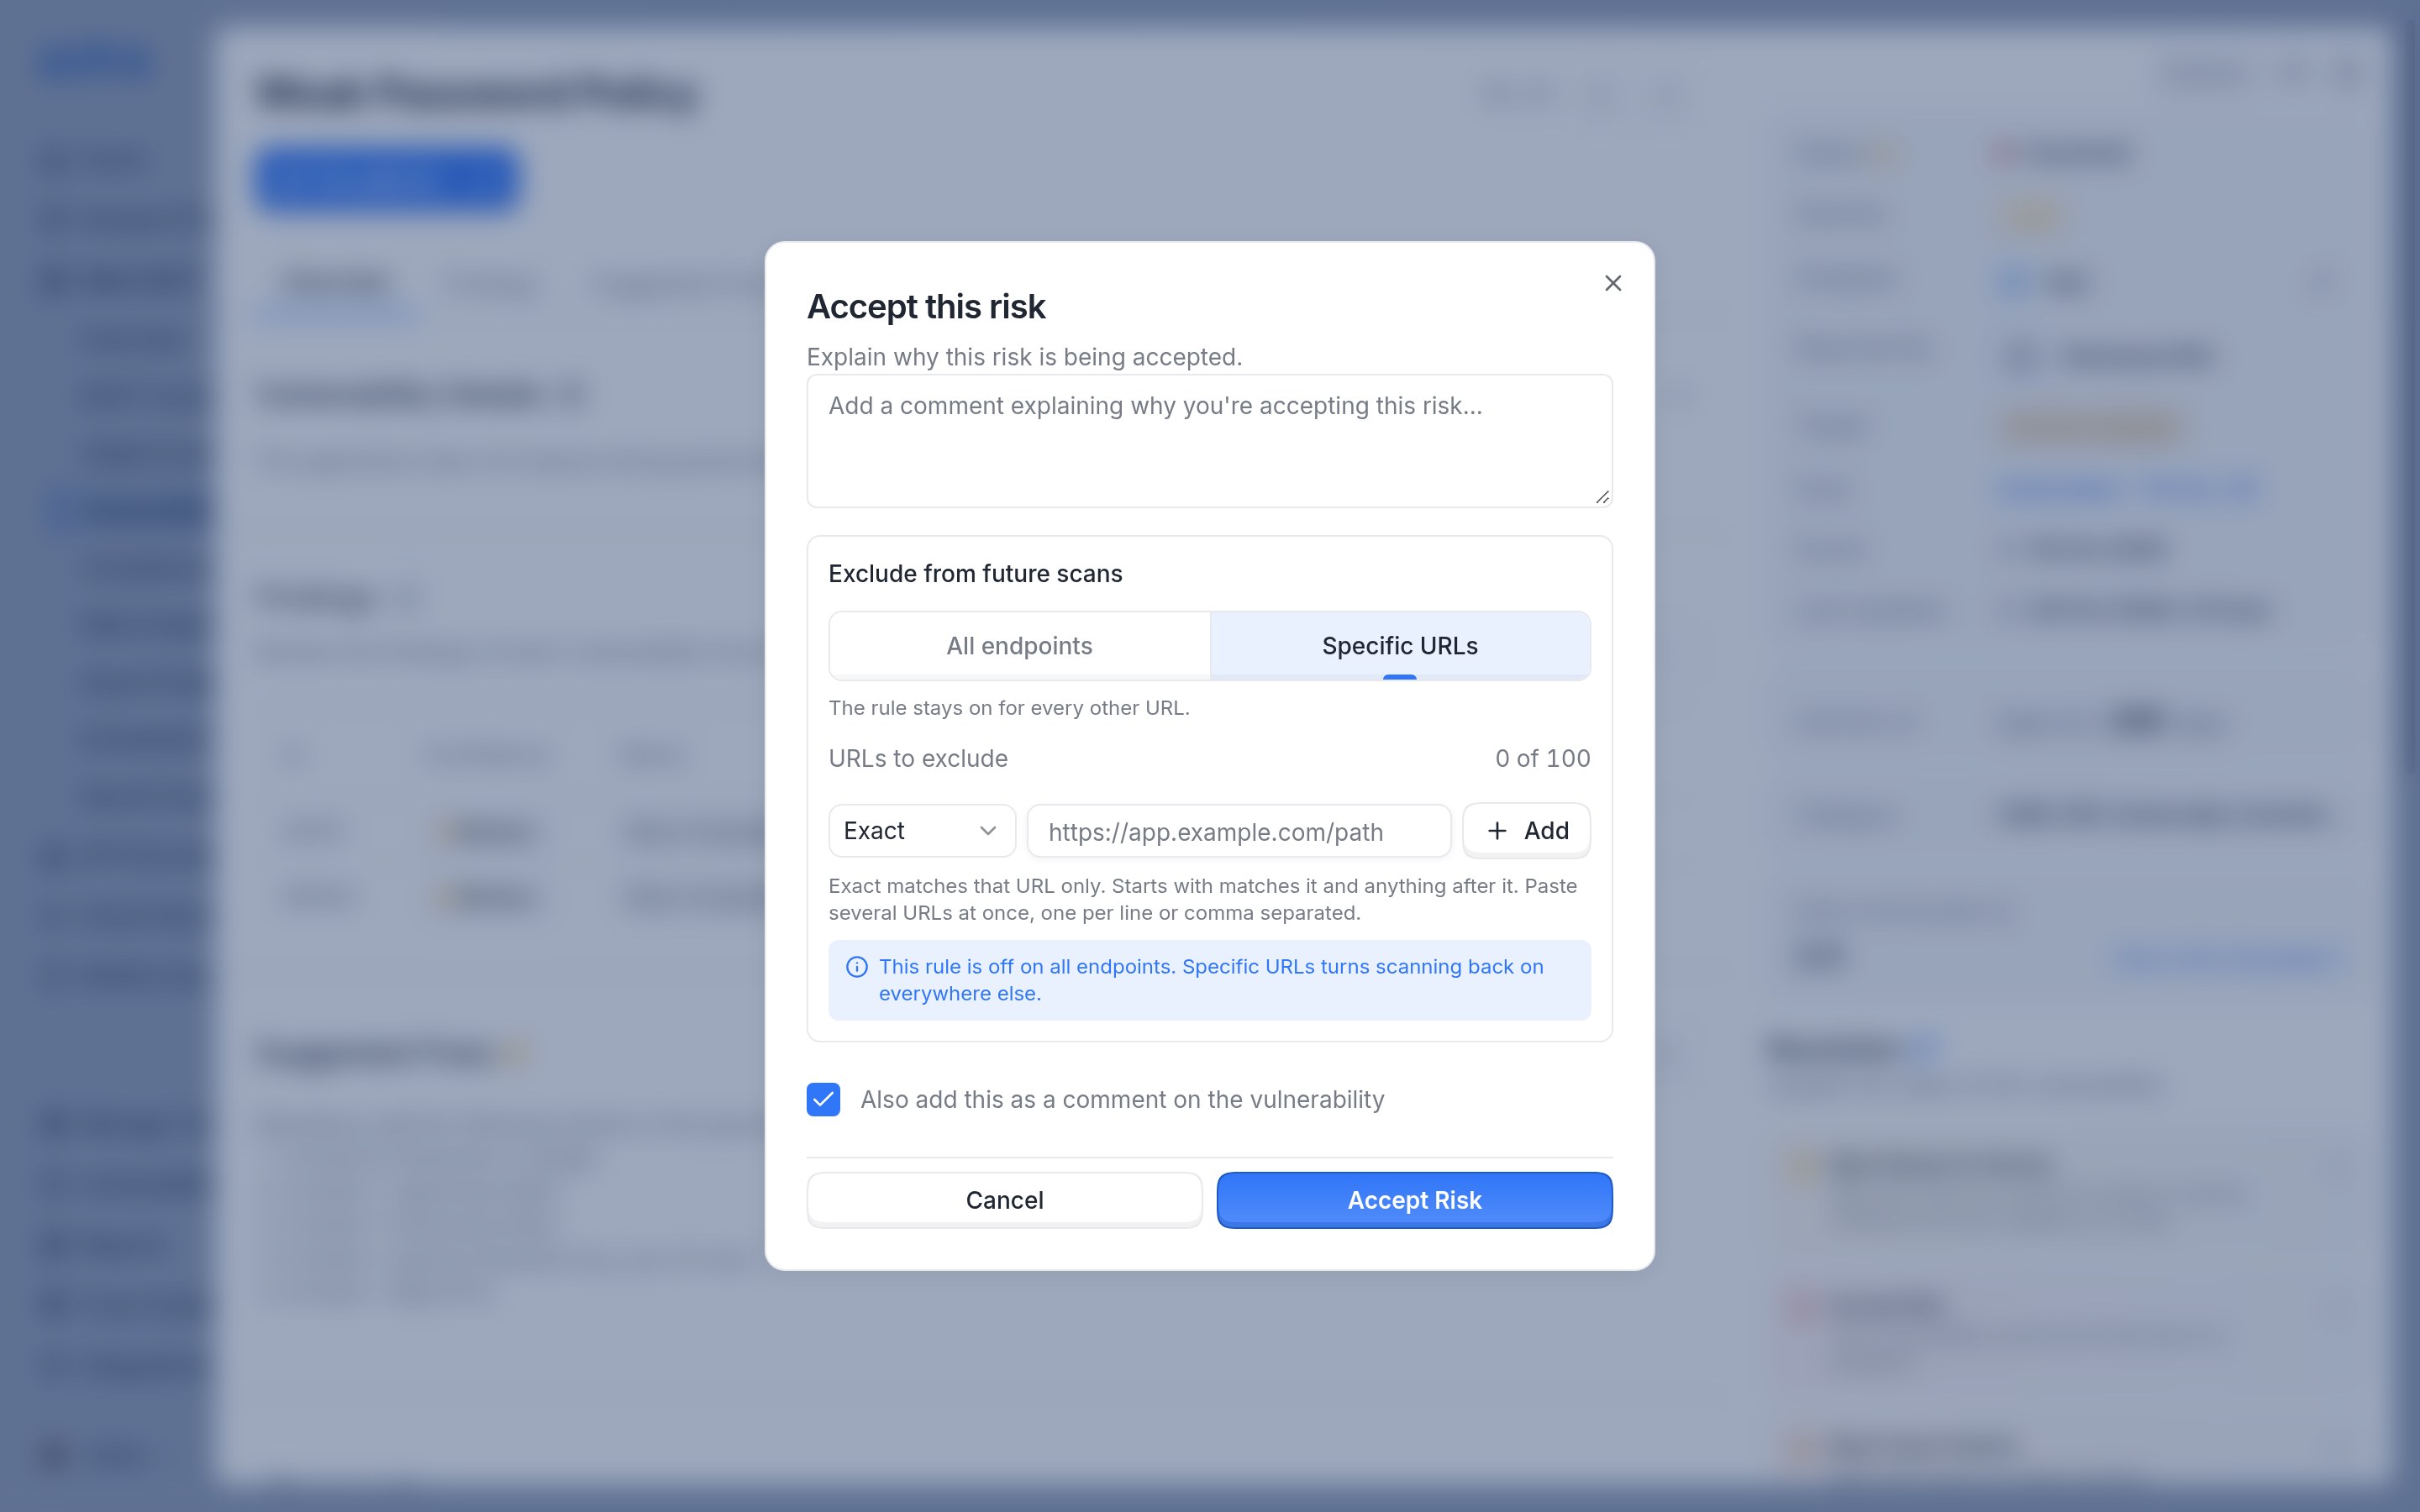
The note shown when the rule is already off on all endpoints and Specific URLs is chosen.
When several vulnerabilities are updated at once. Select them on a scan's Vulnerabilities tab and click Update Status. One switch covers the whole selection, and no URL list is shown. With Specific URLs, each vulnerability is excluded only at its own affected URLs. Vulnerabilities without an affected URL are skipped, and a message says how many.
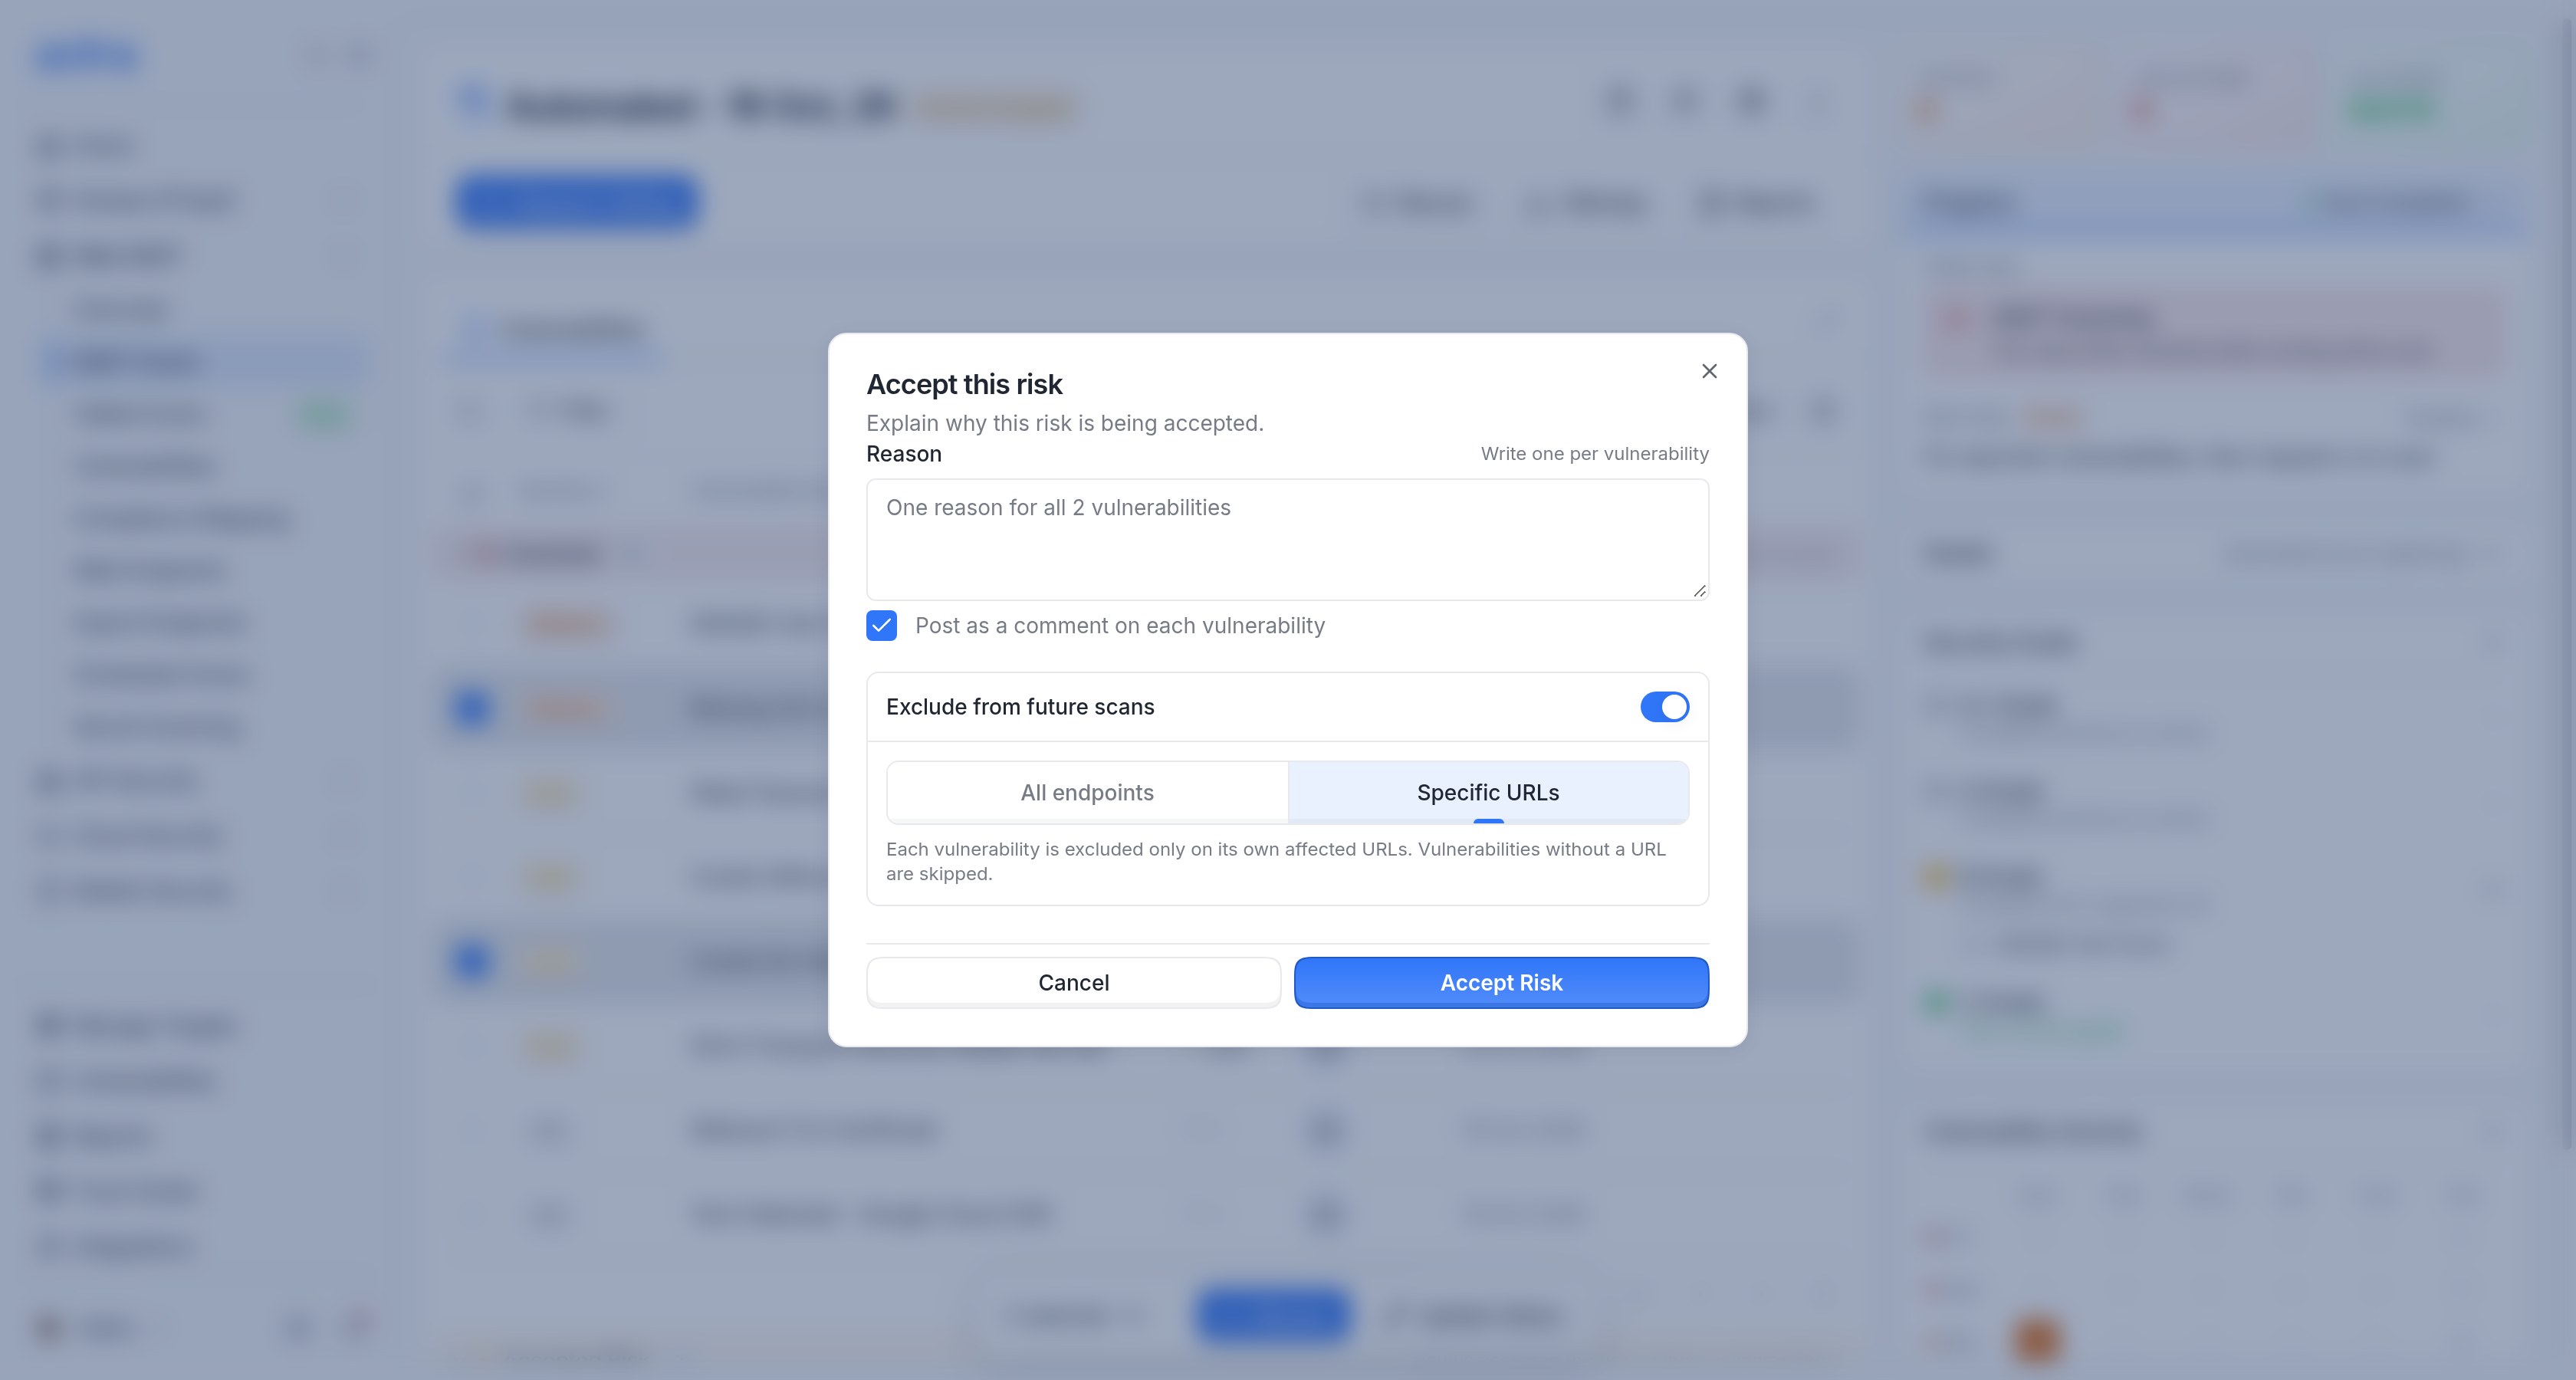
Accepting the risk for two vulnerabilities at once, with Specific URLs.
Manage exclusions in Excluded Scan Rules
Every exclusion for a target is listed in the target's settings, under Excluded Scan Rules in the General section. New exclusions are added from a finding, as described above, and How to add an exclusion on this page shows the same steps. This page is where exclusions are reviewed and changed.
Each row shows the Rule title, what it Applies to, its Status (Active or Paused) and who added it. For Specific URLs, the first URL is shown with a count of the rest, for example +2 more. Hover over it to see every URL, with (starts with) after the ones that use that match type.
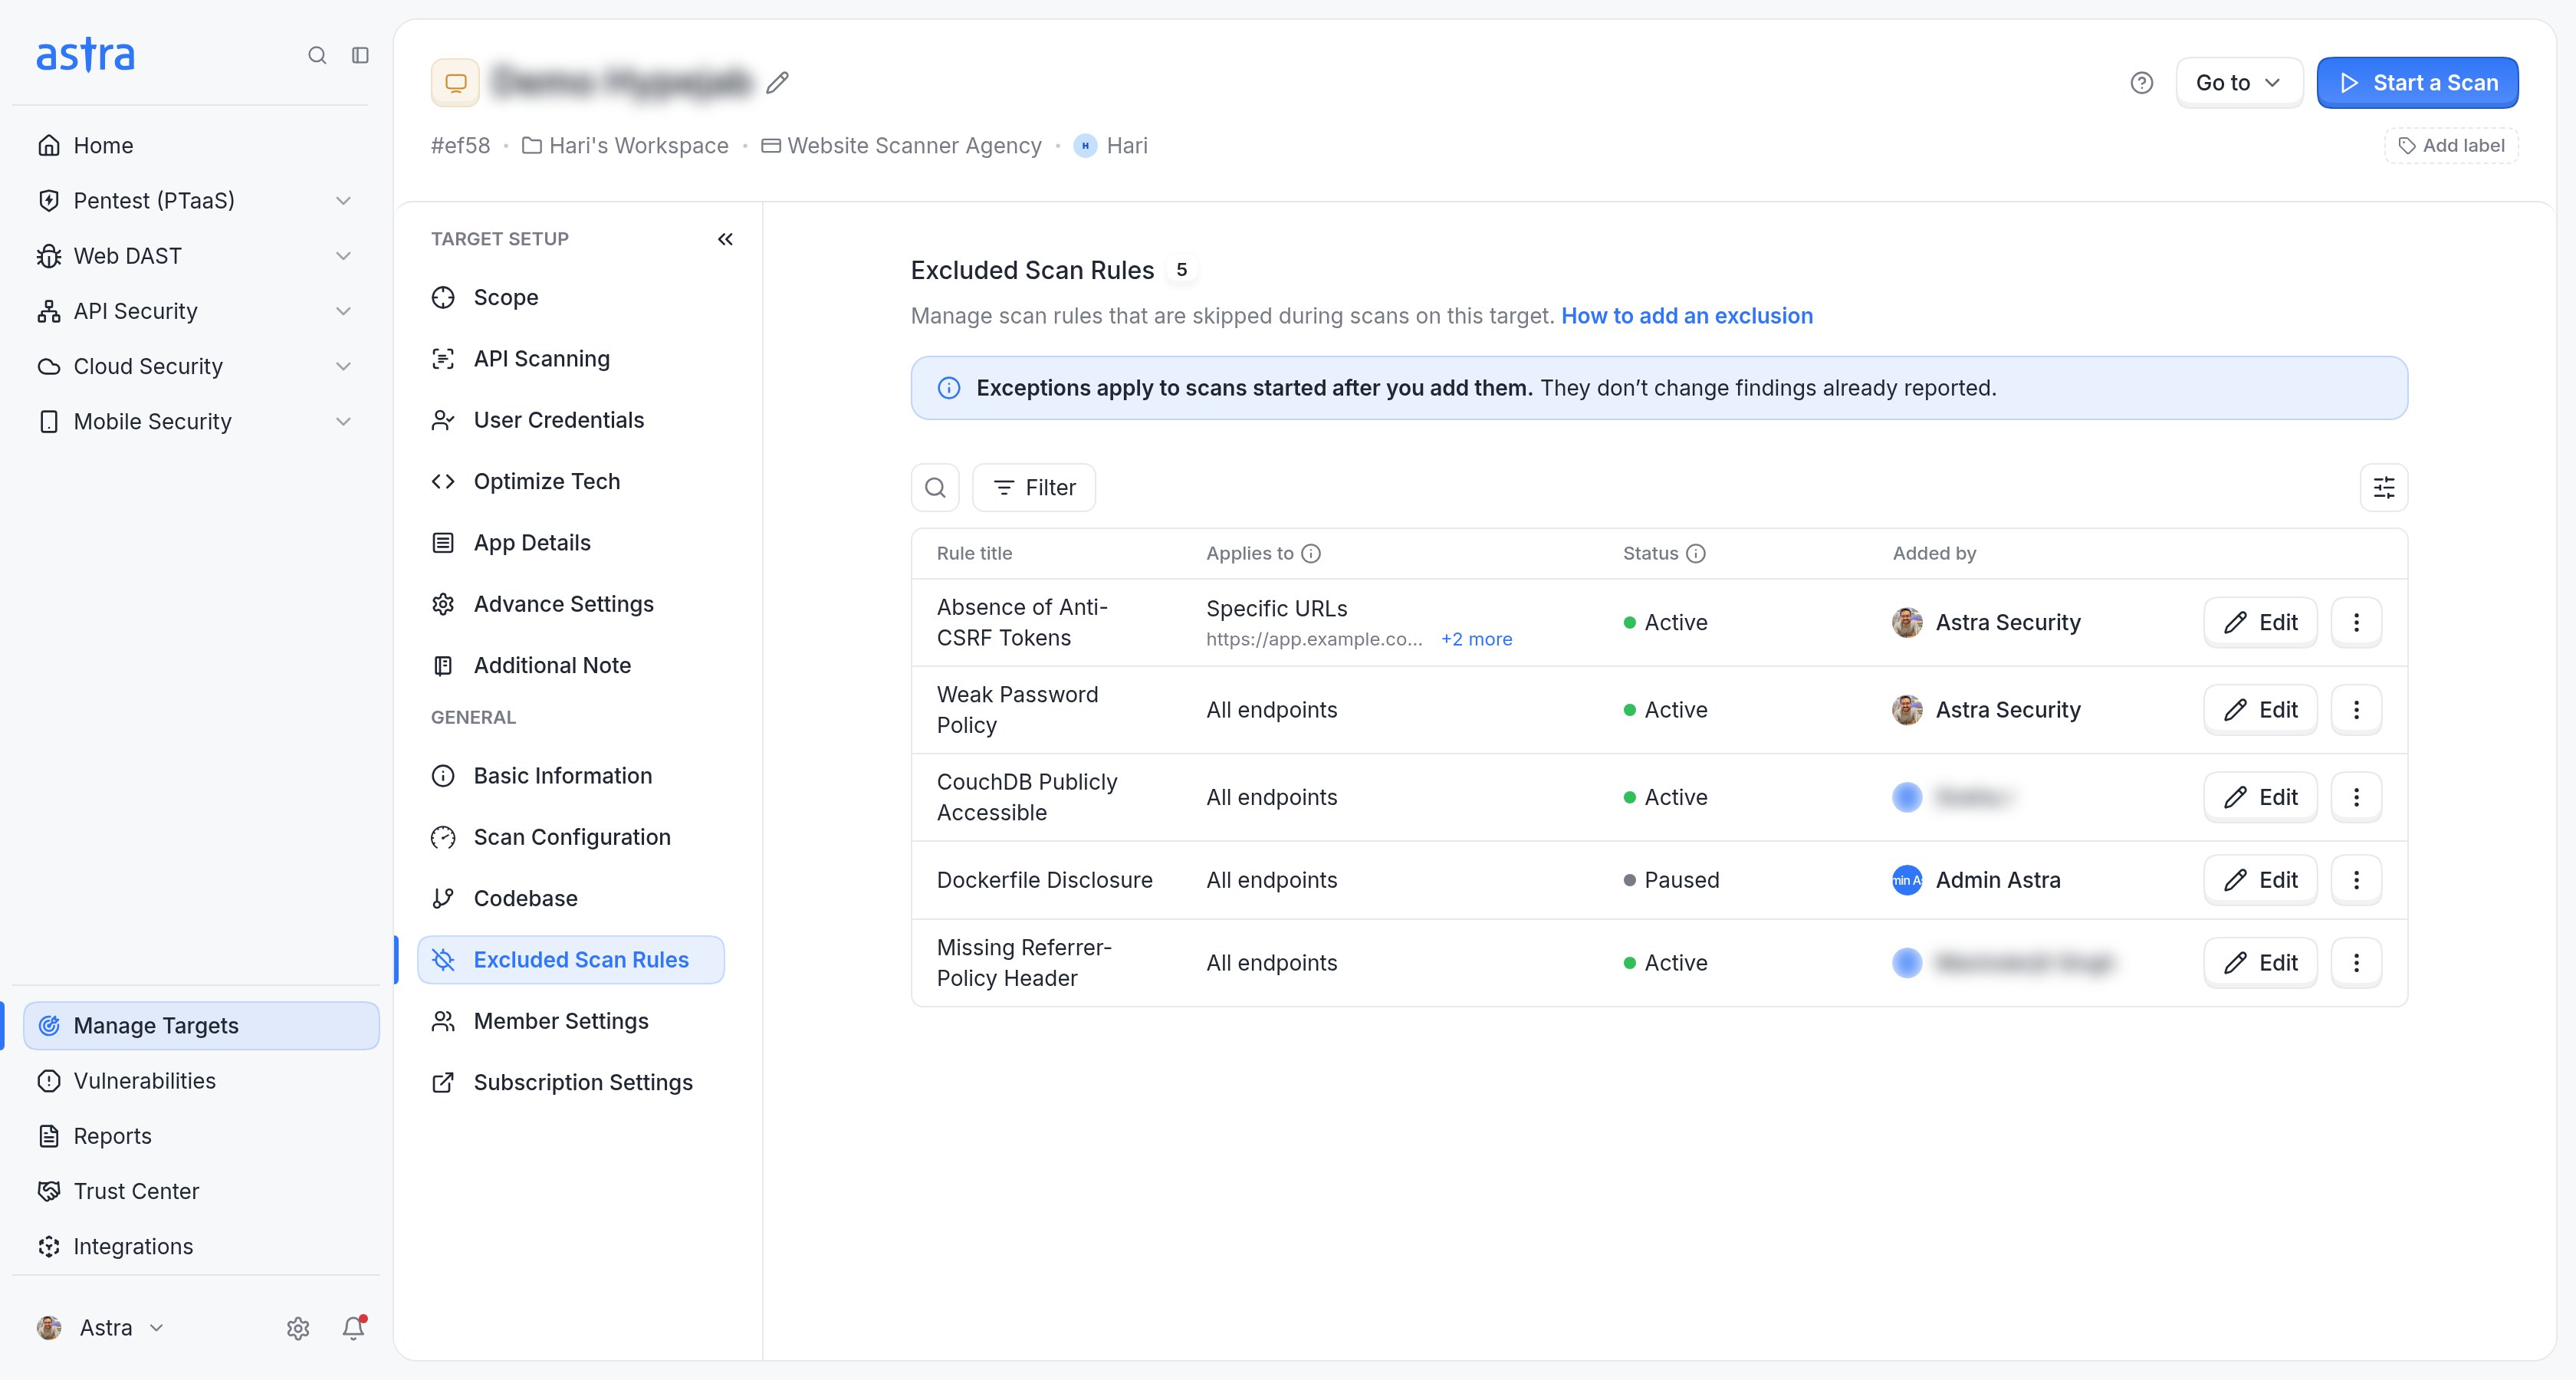
Excluded Scan Rules for a target, with one rule set to Specific URLs and the rest to All endpoints.
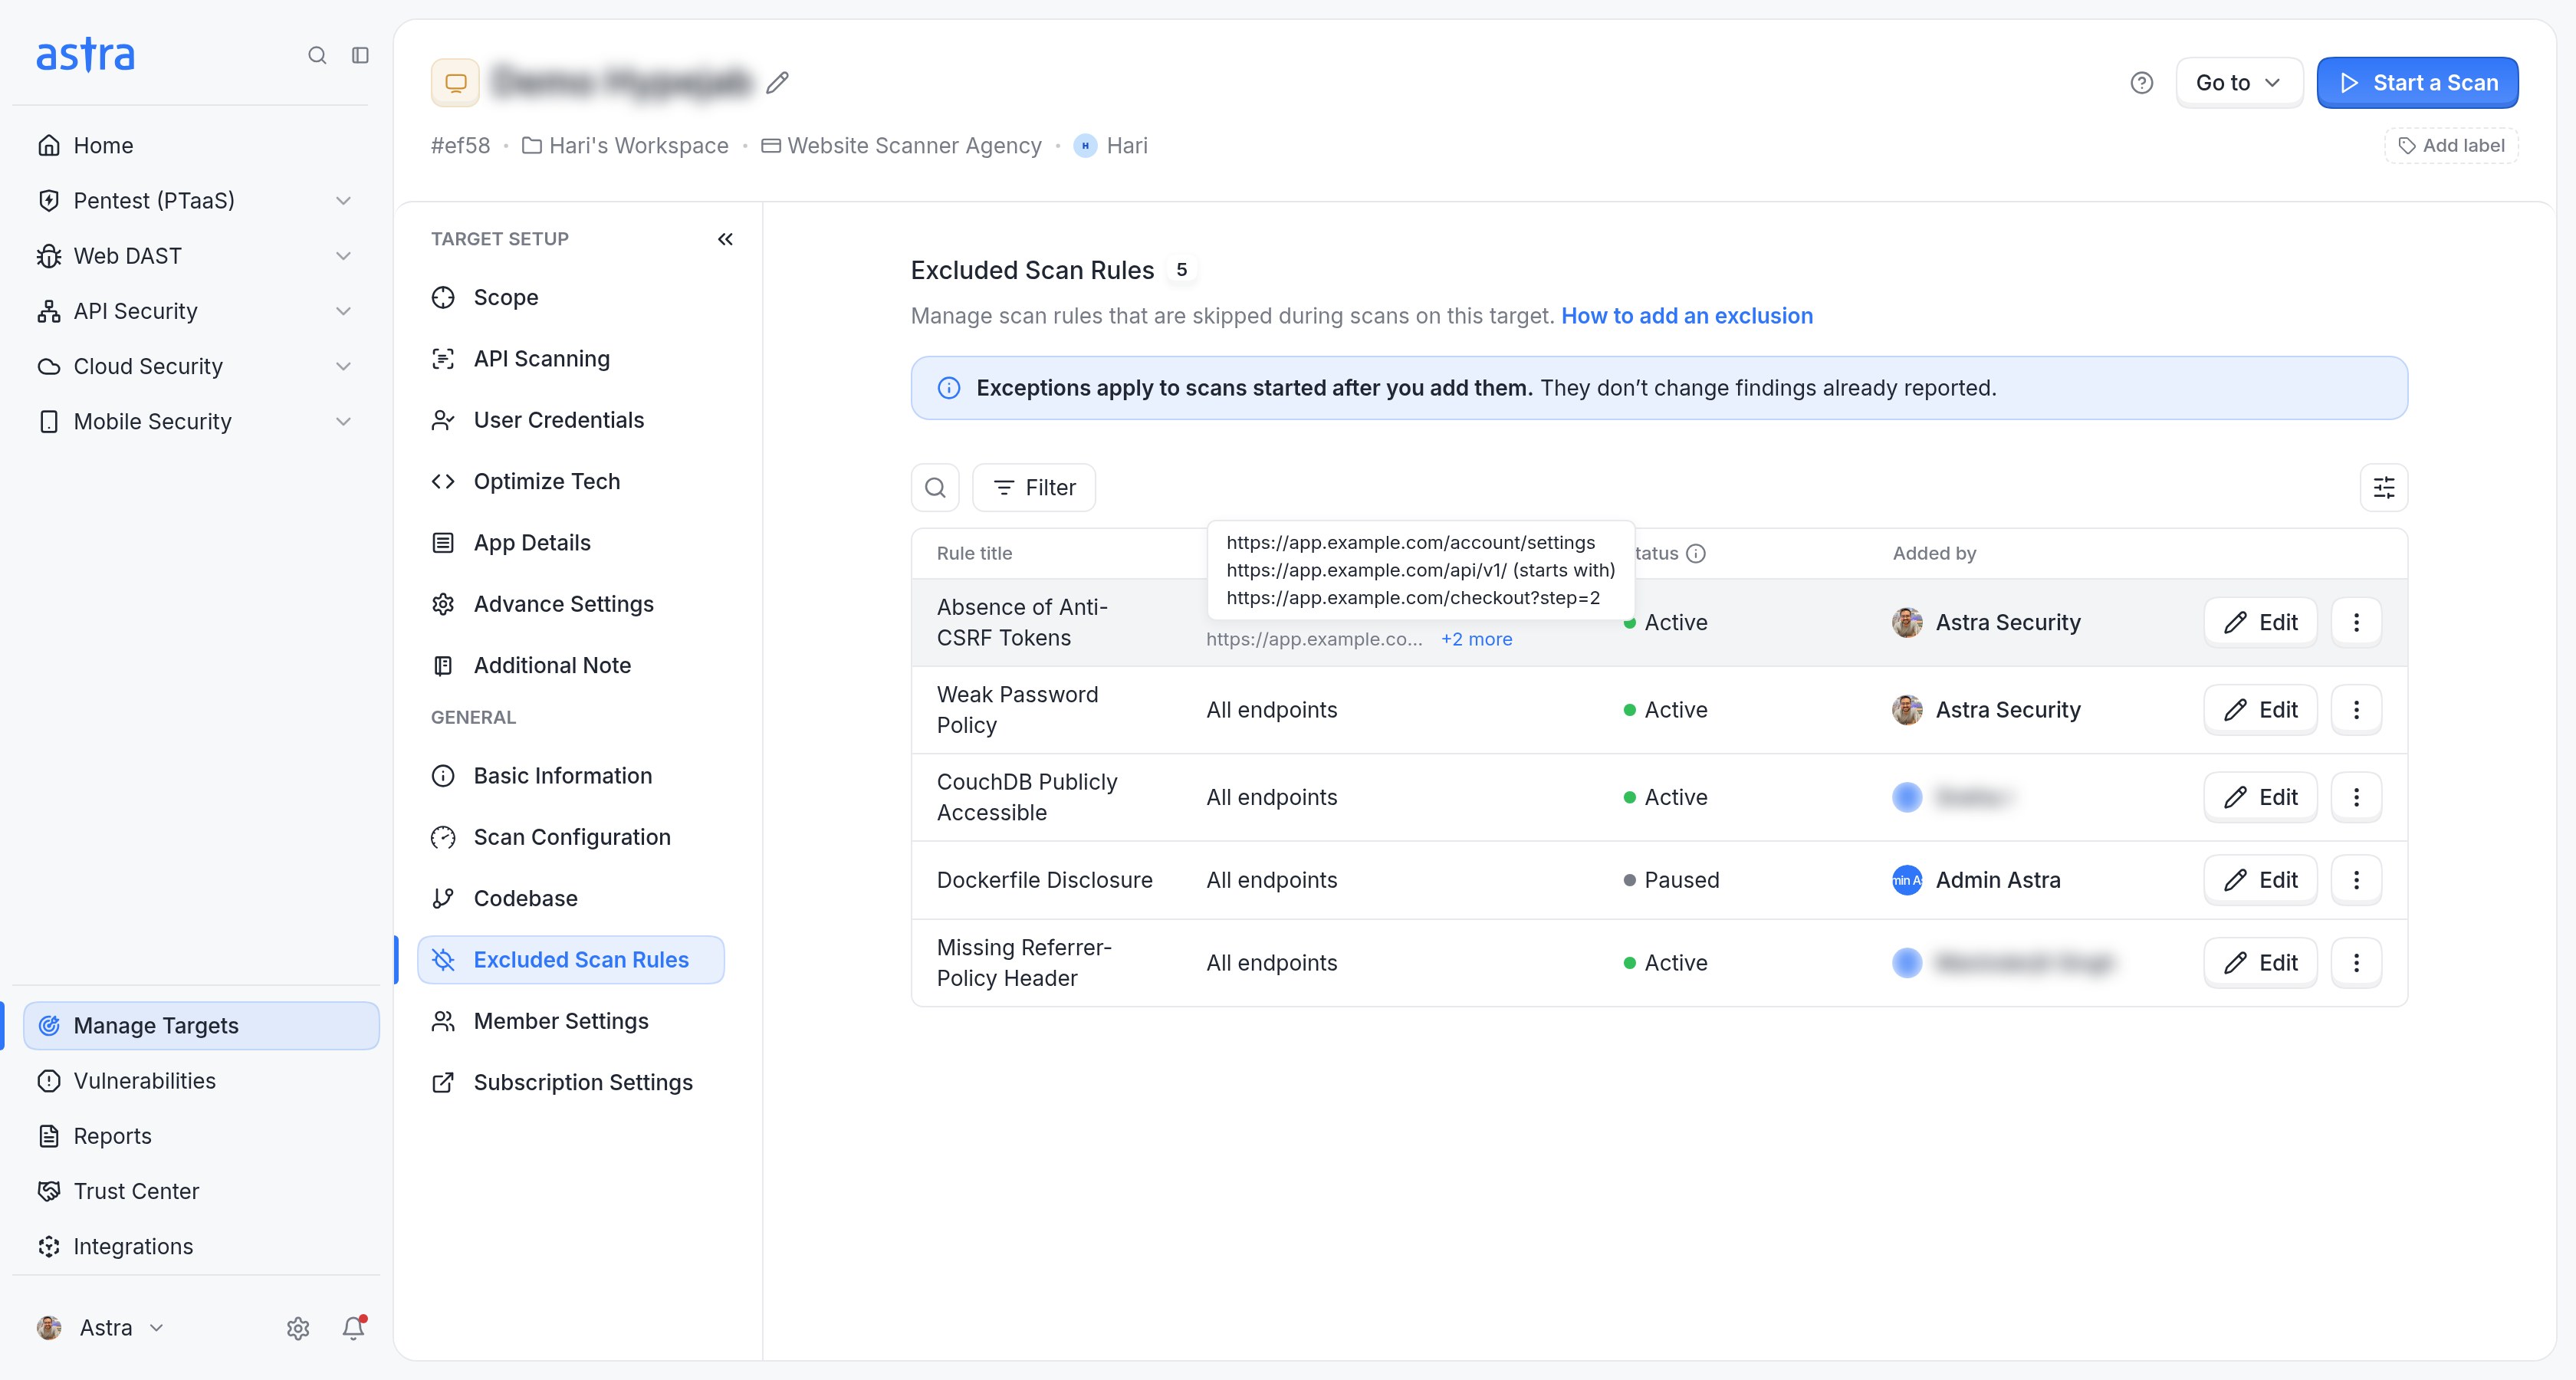
Hovering over the URL count lists every URL in the exclusion.
To change where a rule is excluded:
Click Edit on its row.
In Edit exclusion, switch between All endpoints and Specific URLs, and add, change or remove URLs the same way as in the vulnerability dialog.
Click Save changes. The change applies as soon as it's saved, including to a scan that's already running.
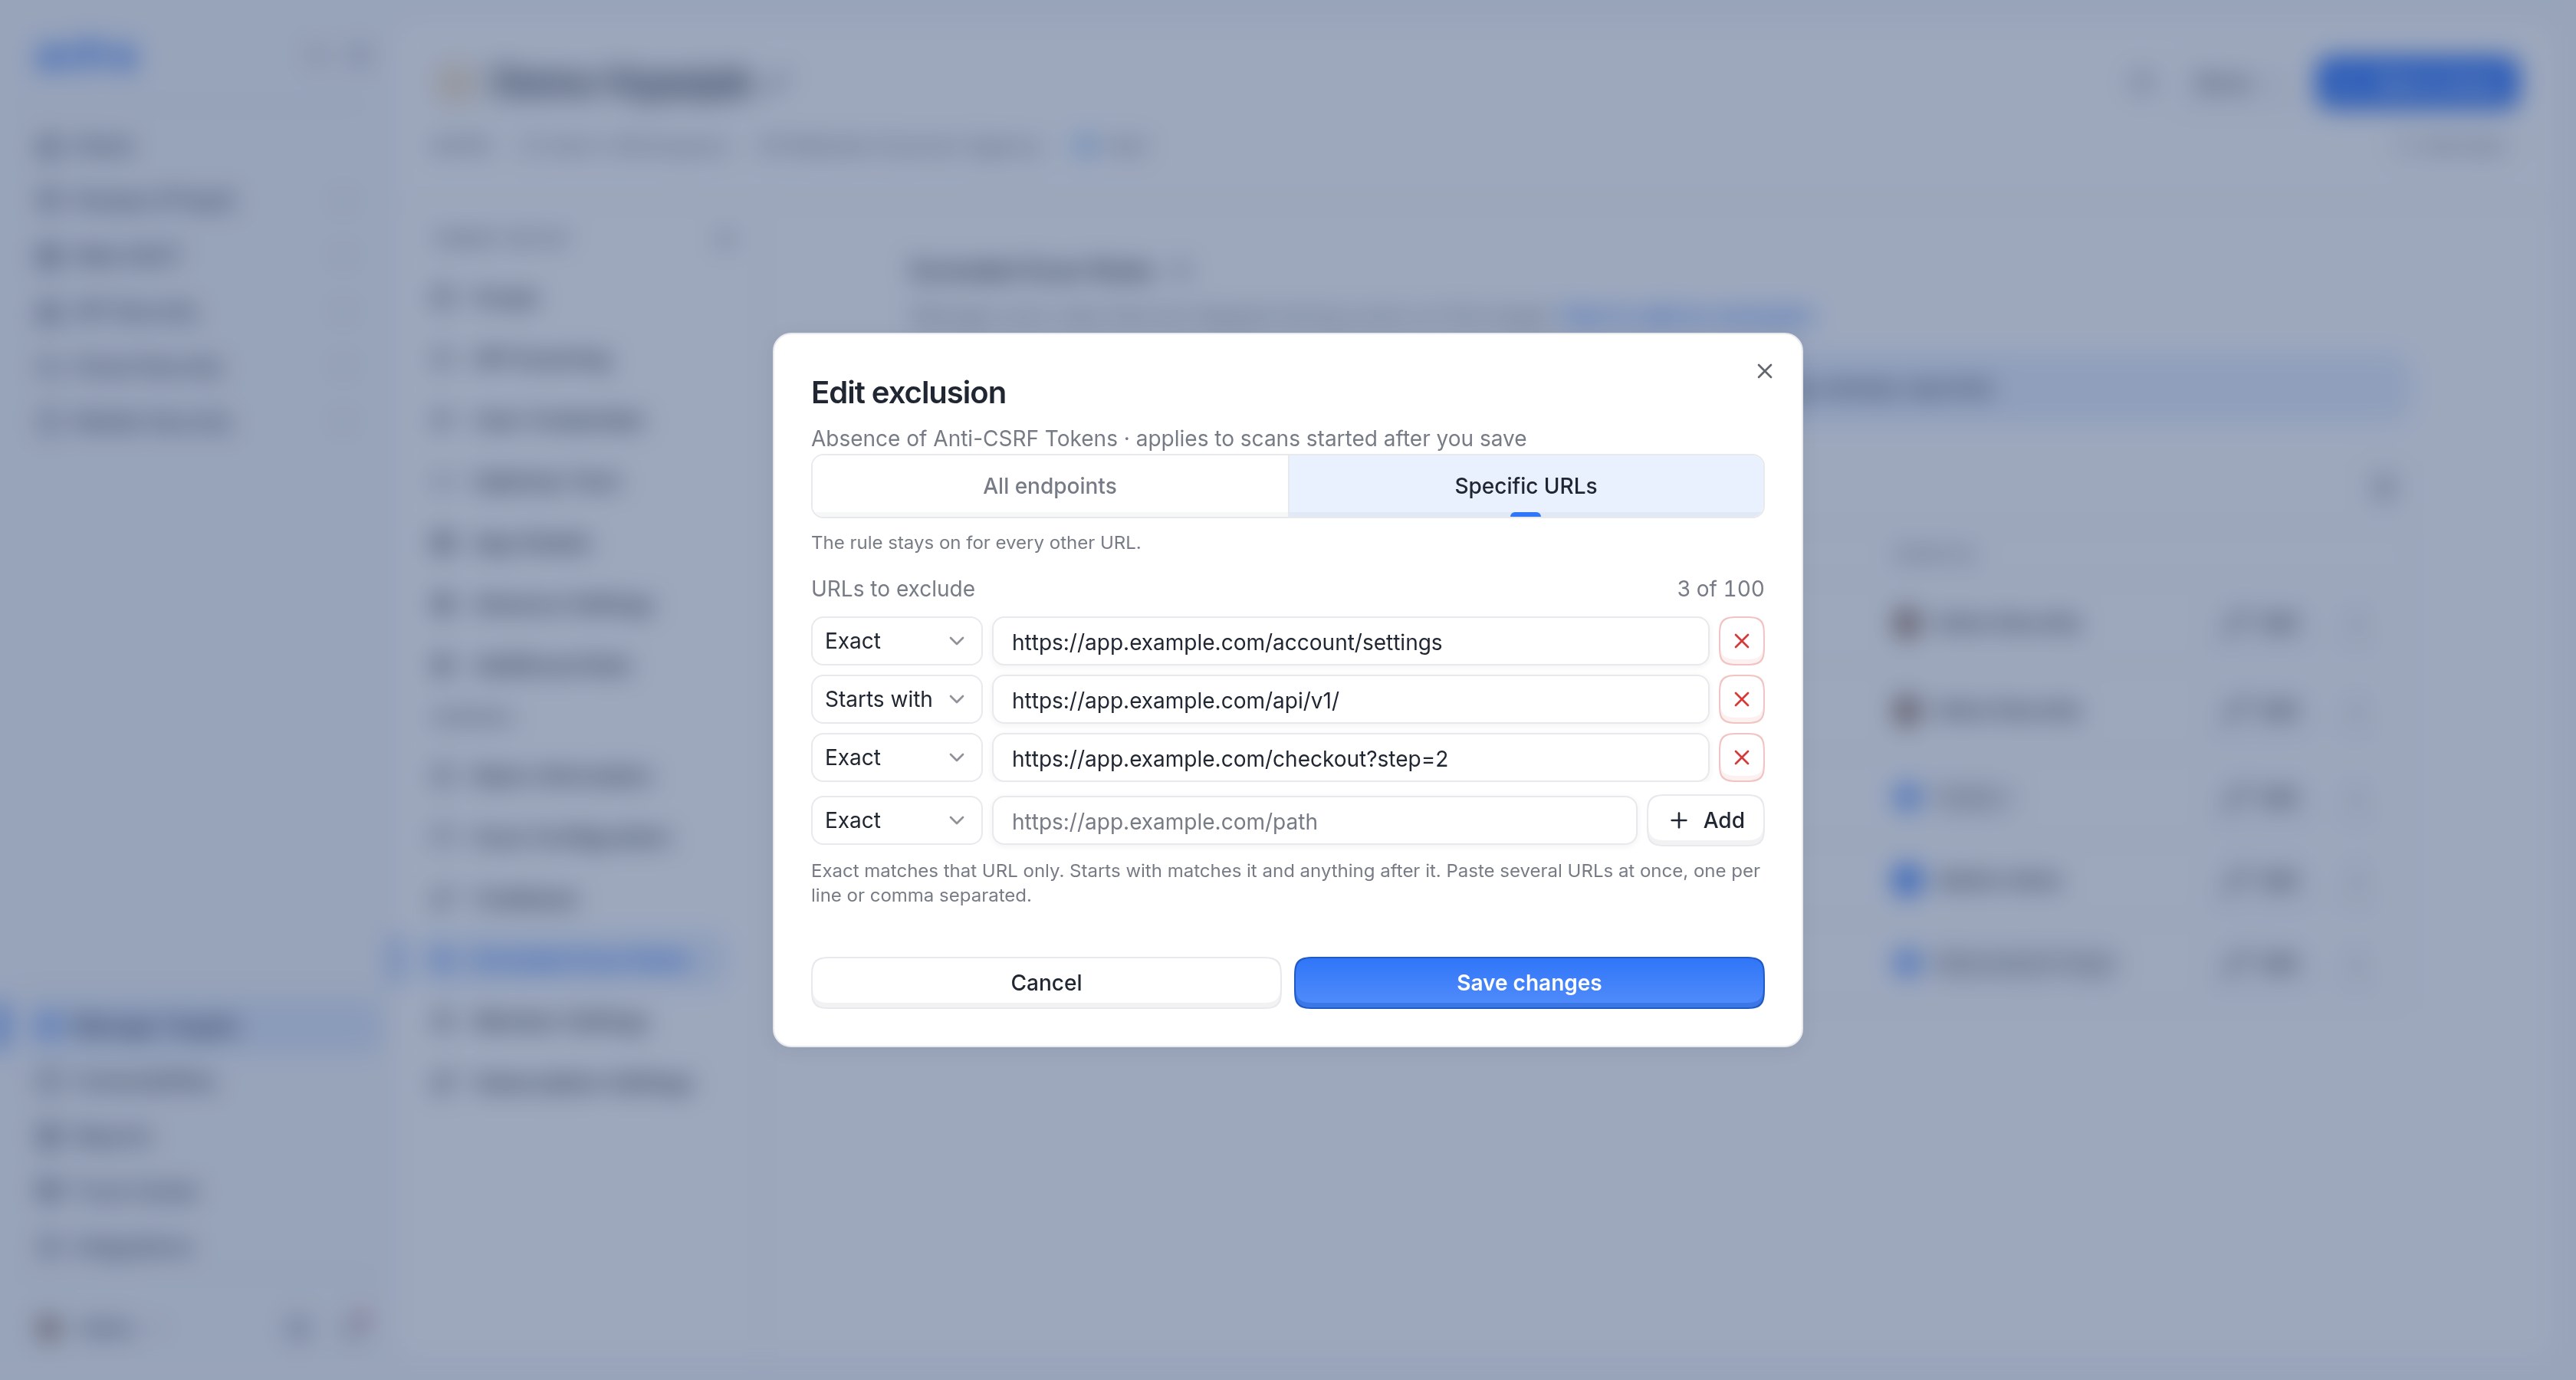
The Edit exclusion dialog, with the saved URLs.
Switching a rule from Specific URLs to All endpoints asks Turn this rule off on all endpoints? first, because the saved URLs are removed. Click Turn off everywhere to confirm.
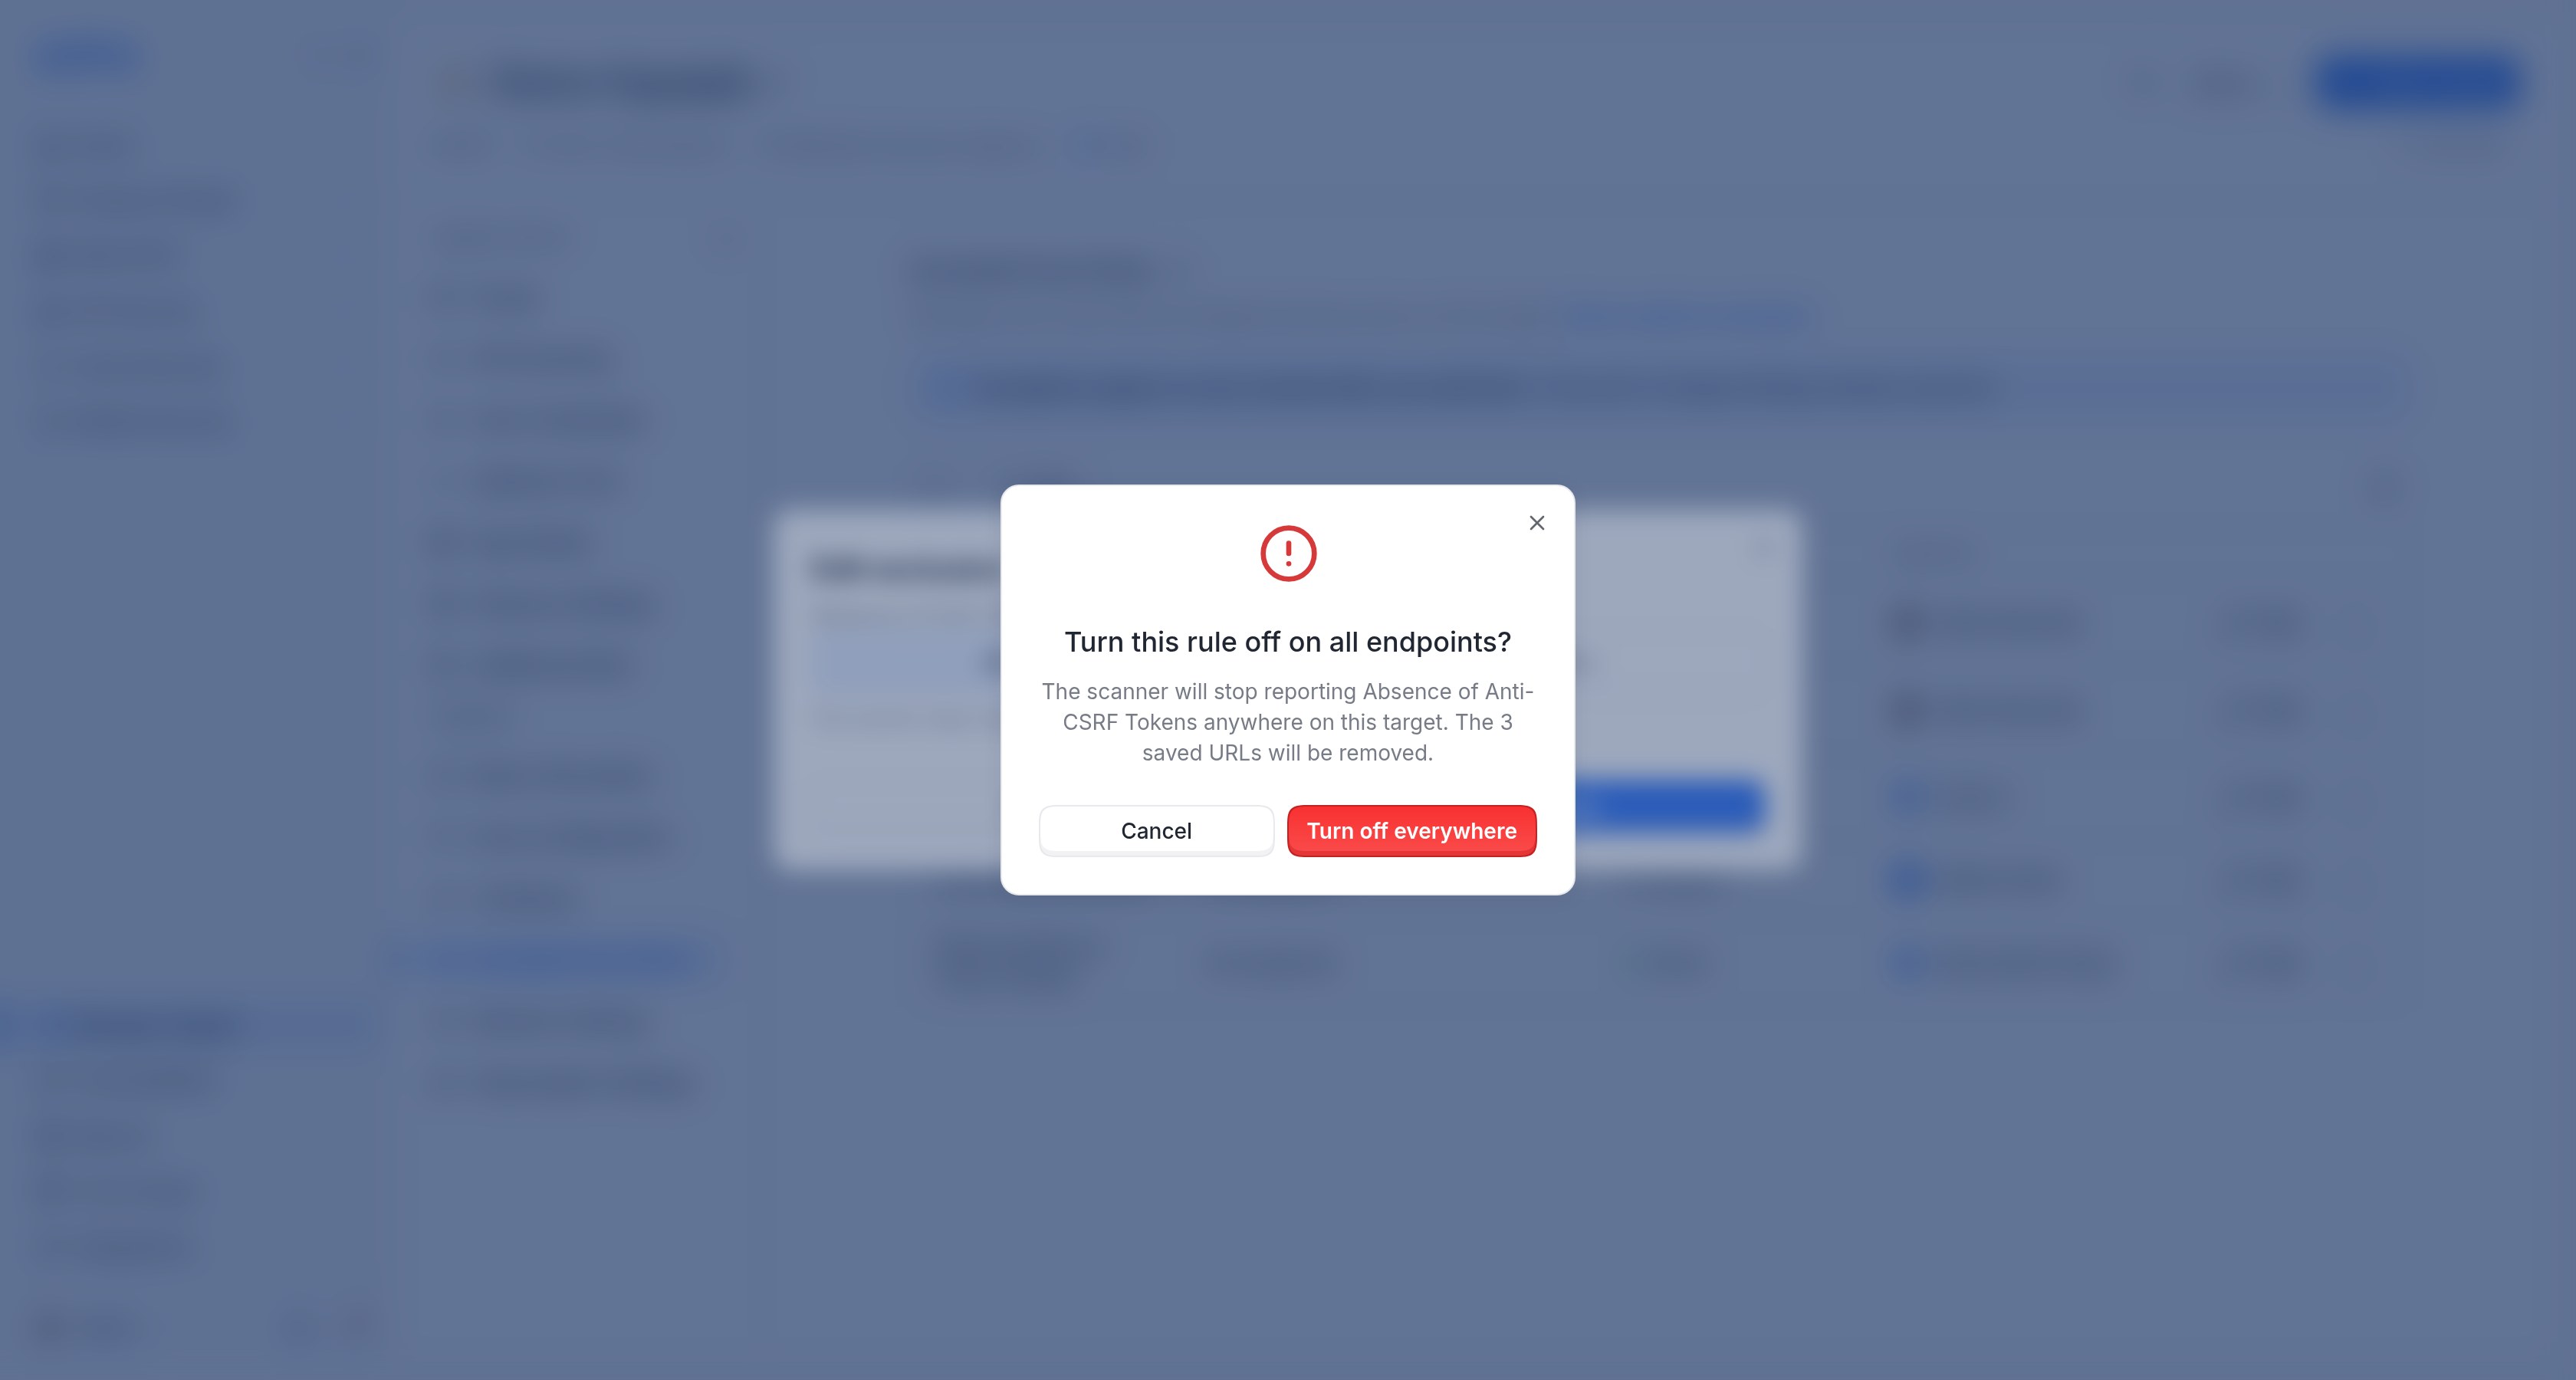
The confirmation before a rule is turned off on all endpoints.
The ⋮ menu on each row has the other actions:
Add note or View note: keep a note on why the rule is excluded.
Pause exception: scans evaluate the rule again while it's paused, and the exclusion keeps its settings. Activate exception turns it back on.
Delete: removes the exclusion, so later scans report the rule again.
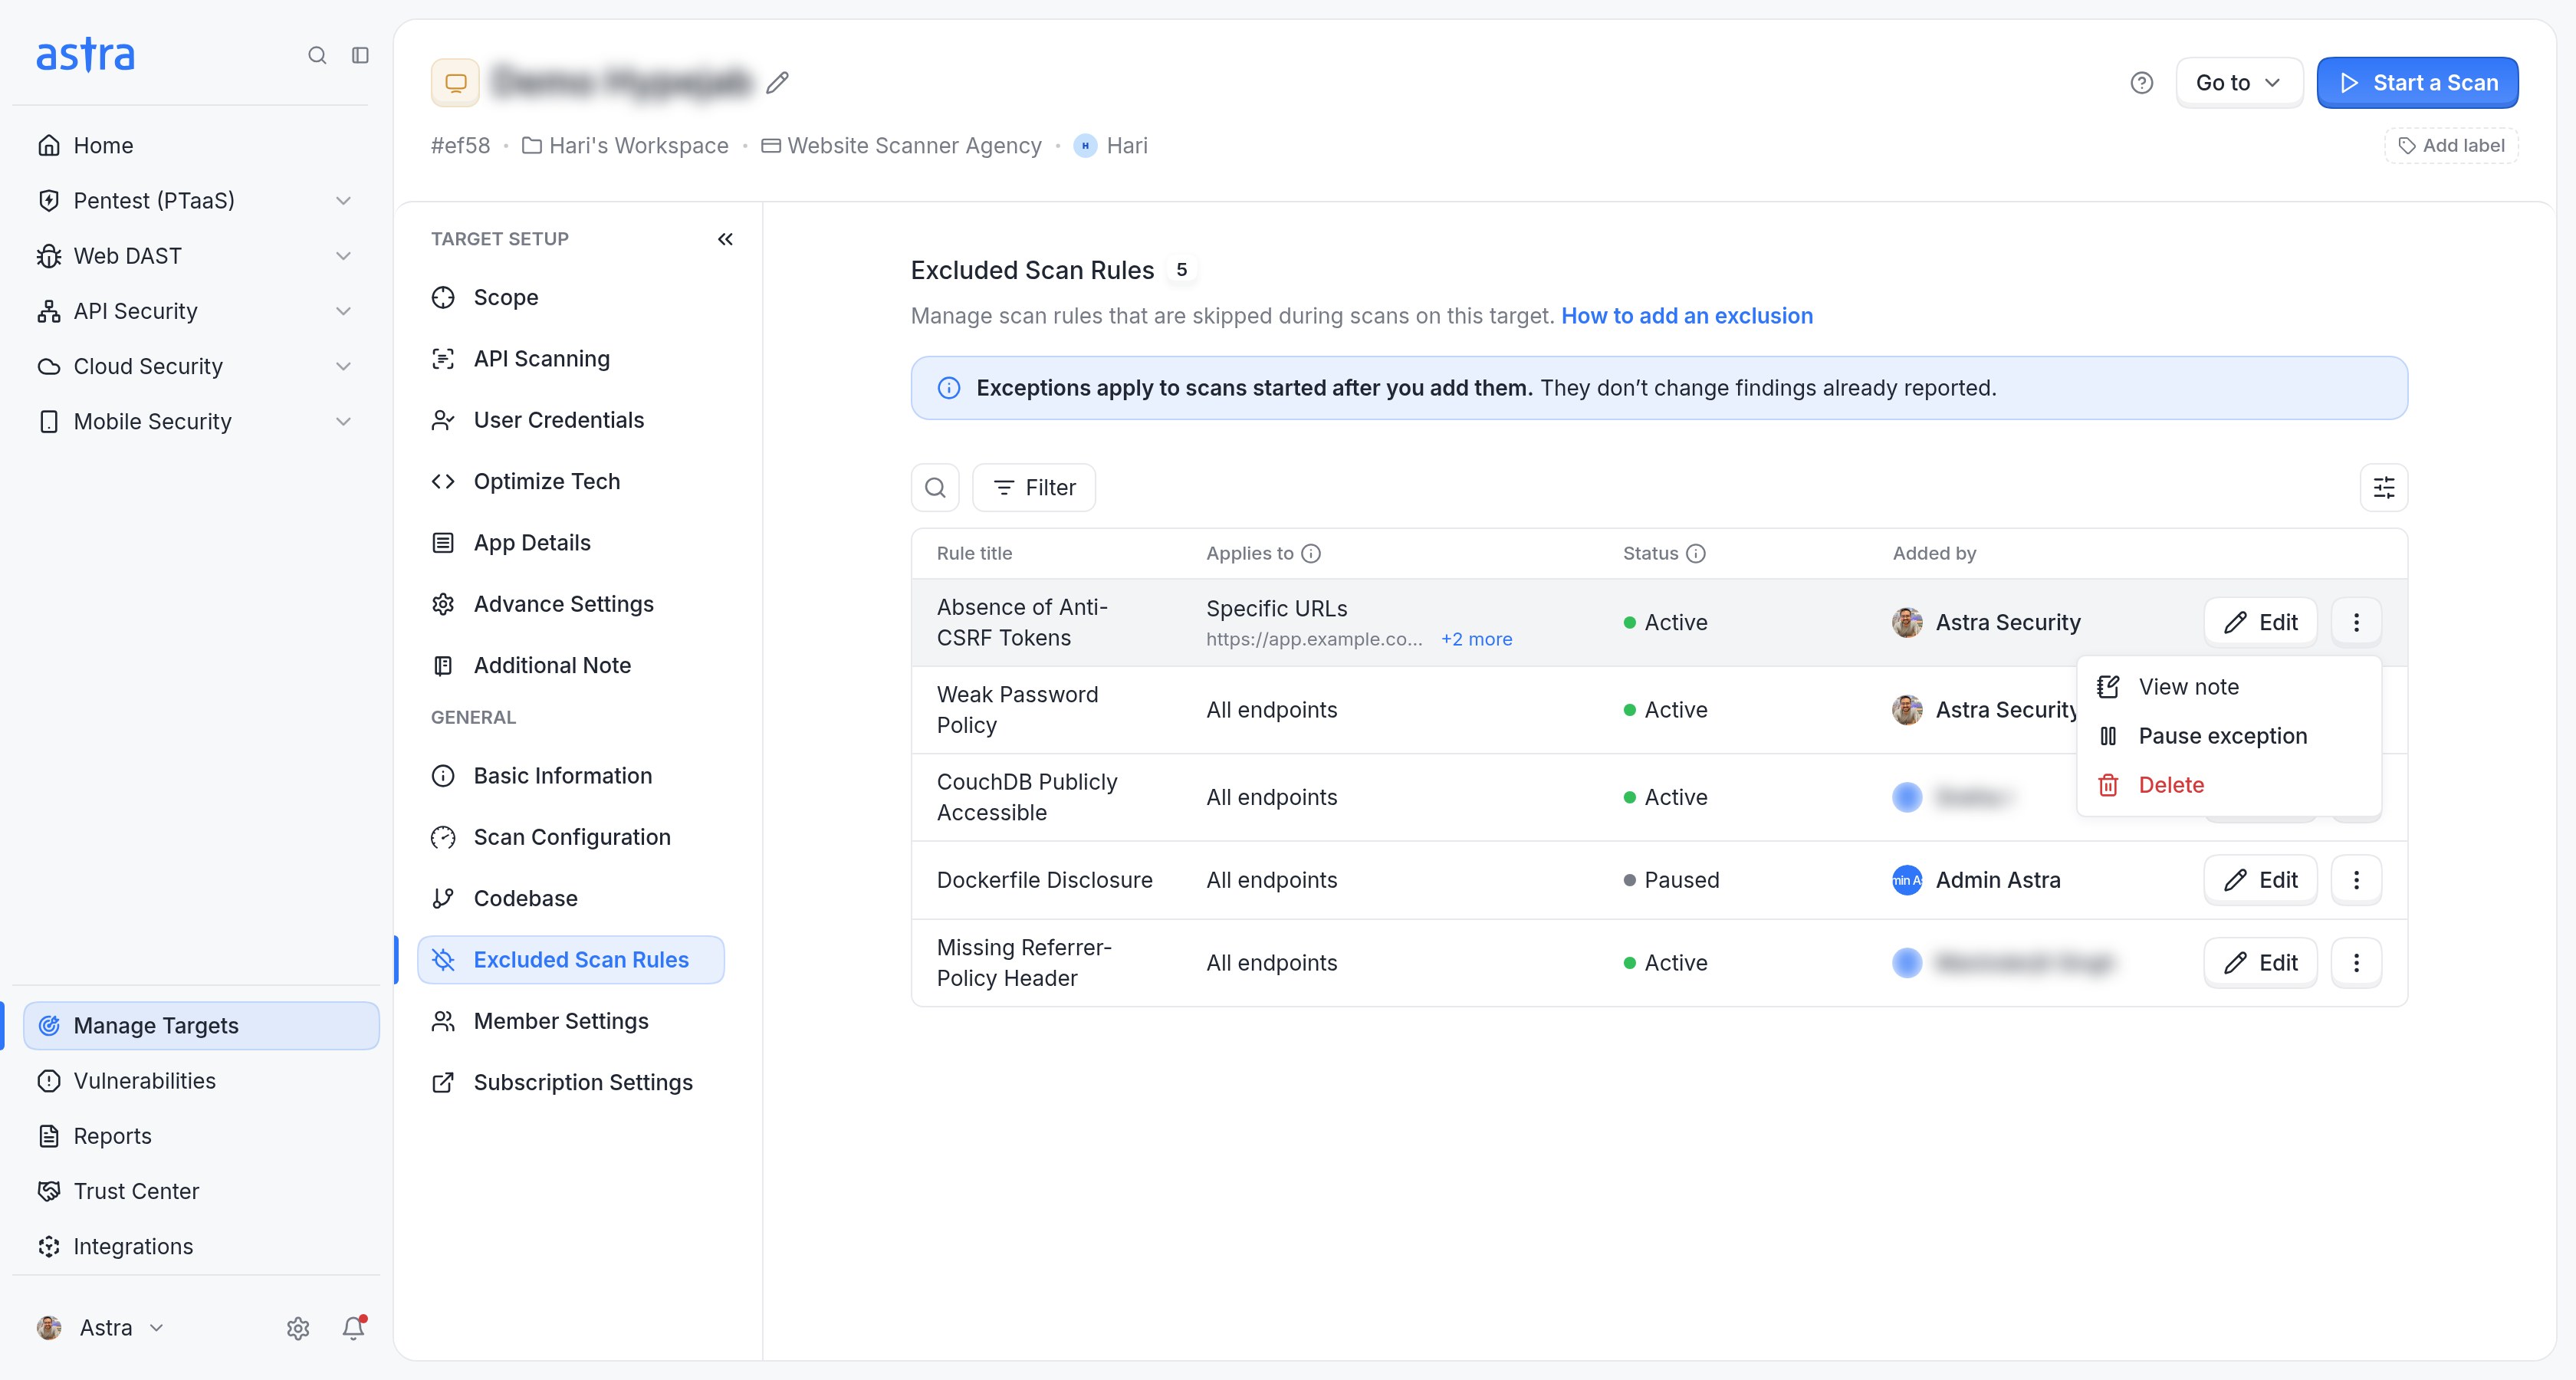
The row menu, with View note, Pause exception and Delete.
Unmarking a false positive also removes the exclusion saved for that rule on the target.
Troubleshooting
An excluded rule is still reported in new scans
Check that the rule is listed under Excluded Scan Rules for the same target. Exclusions apply to one target only.
Check that its status is Active. A paused exclusion doesn't skip the rule.
If the exclusion applies to Specific URLs, check that the URL where the finding appeared is in its list. Click Edit to add it, or switch the rule to All endpoints.
Exclusions apply as soon as they're saved, including to a scan that's already running. Findings reported before the exclusion was saved stay as they are.
A brute-force rule needs to be tested again
Open Excluded Scan Rules, then use the row's ⋮ menu. Pause exception tests the rule again until the exclusion is activated, and Delete removes the exclusion. Either way, the rule is tested from the next scan onward.
FAQ
Can several URLs be excluded under one rule?
Yes. Choose Specific URLs and add up to 100 URLs to the same exclusion, or paste a list of them at once. An existing exclusion can be changed from Excluded Scan Rules with Edit.
Where are scan exclusions set up for a target?
Exclusions are added from a vulnerability, with Exclude from future scans when accepting the risk or marking a false positive. They're then listed, edited, paused and deleted in the target's settings under Excluded Scan Rules.
Does an exclusion stop the scanner from scanning those URLs?
No. An exclusion only stops one rule from being reported. Every other check still runs at those URLs.